Single sign-on · Setup guides
Auth0
Use Auth0 as a SAML identity provider for OrbitID by enabling the SAML2 Web App addon on an Auth0 application. You need access to the Auth0 dashboard.
Step 1: Create application
From your Auth0 dashboard, click Applications from the left navigation menu.
If your application is already created, choose it from the list and move to the next step.
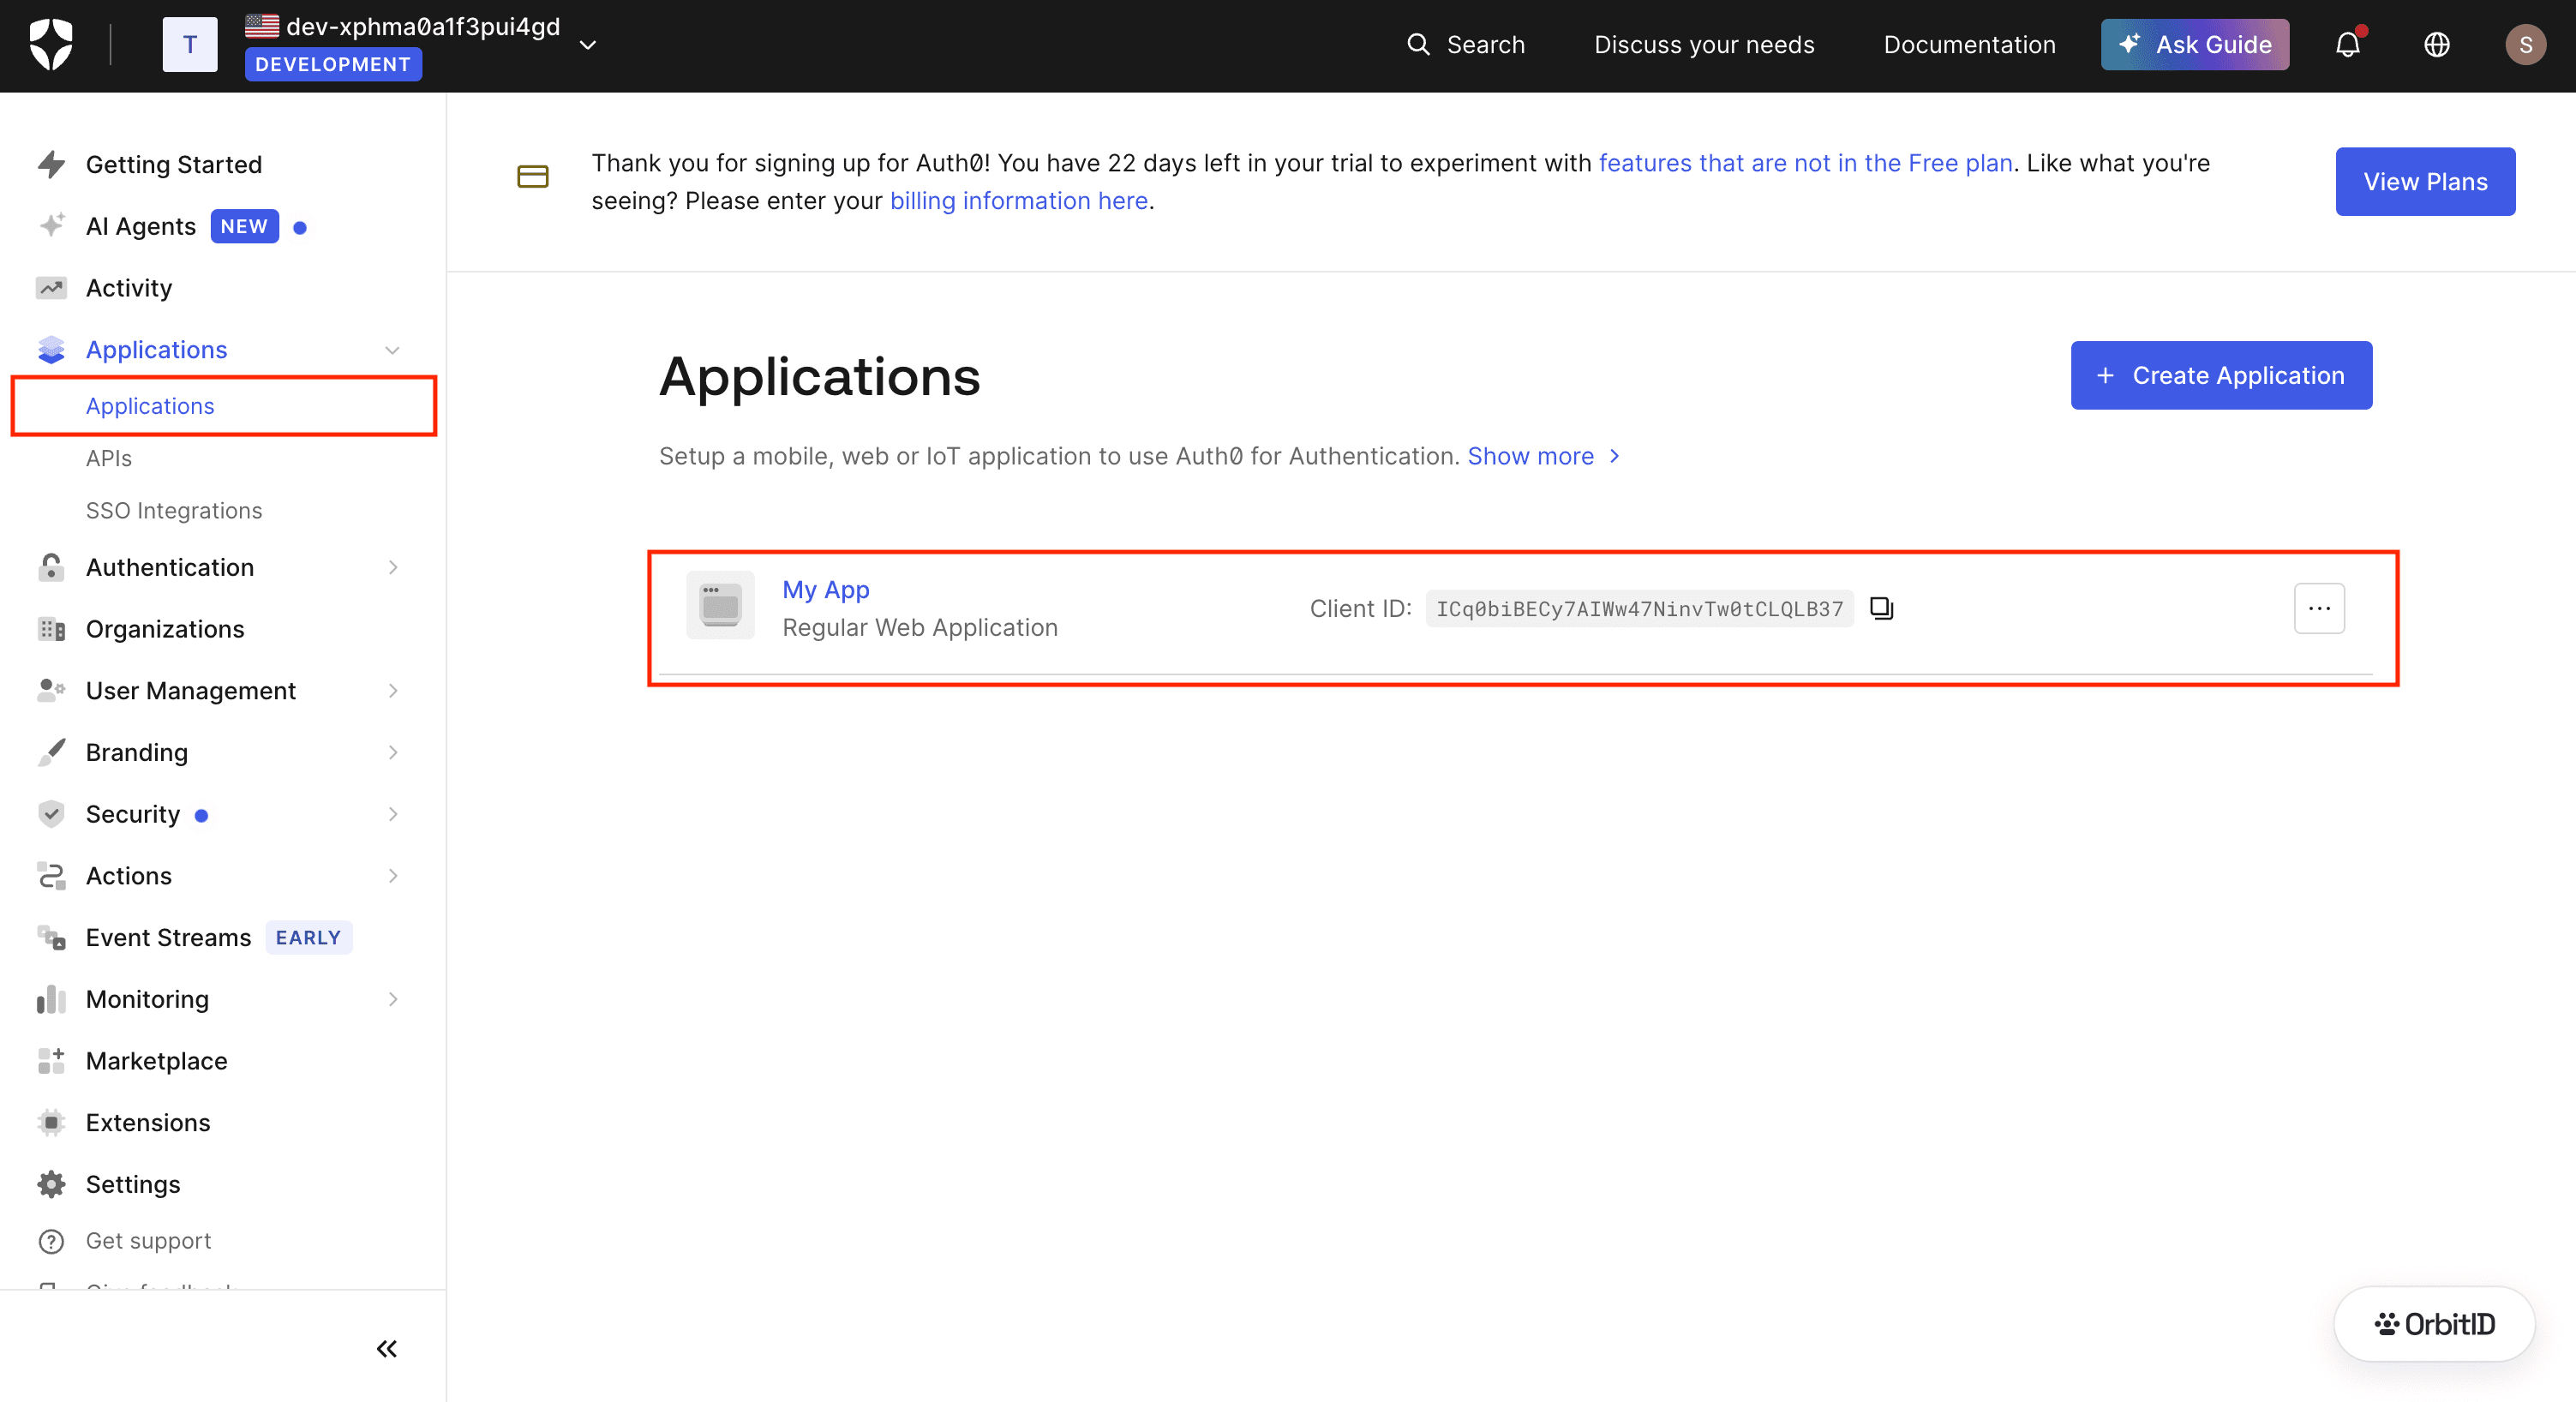
If you haven't created a SAML application, click the Create Application button to create a new application.
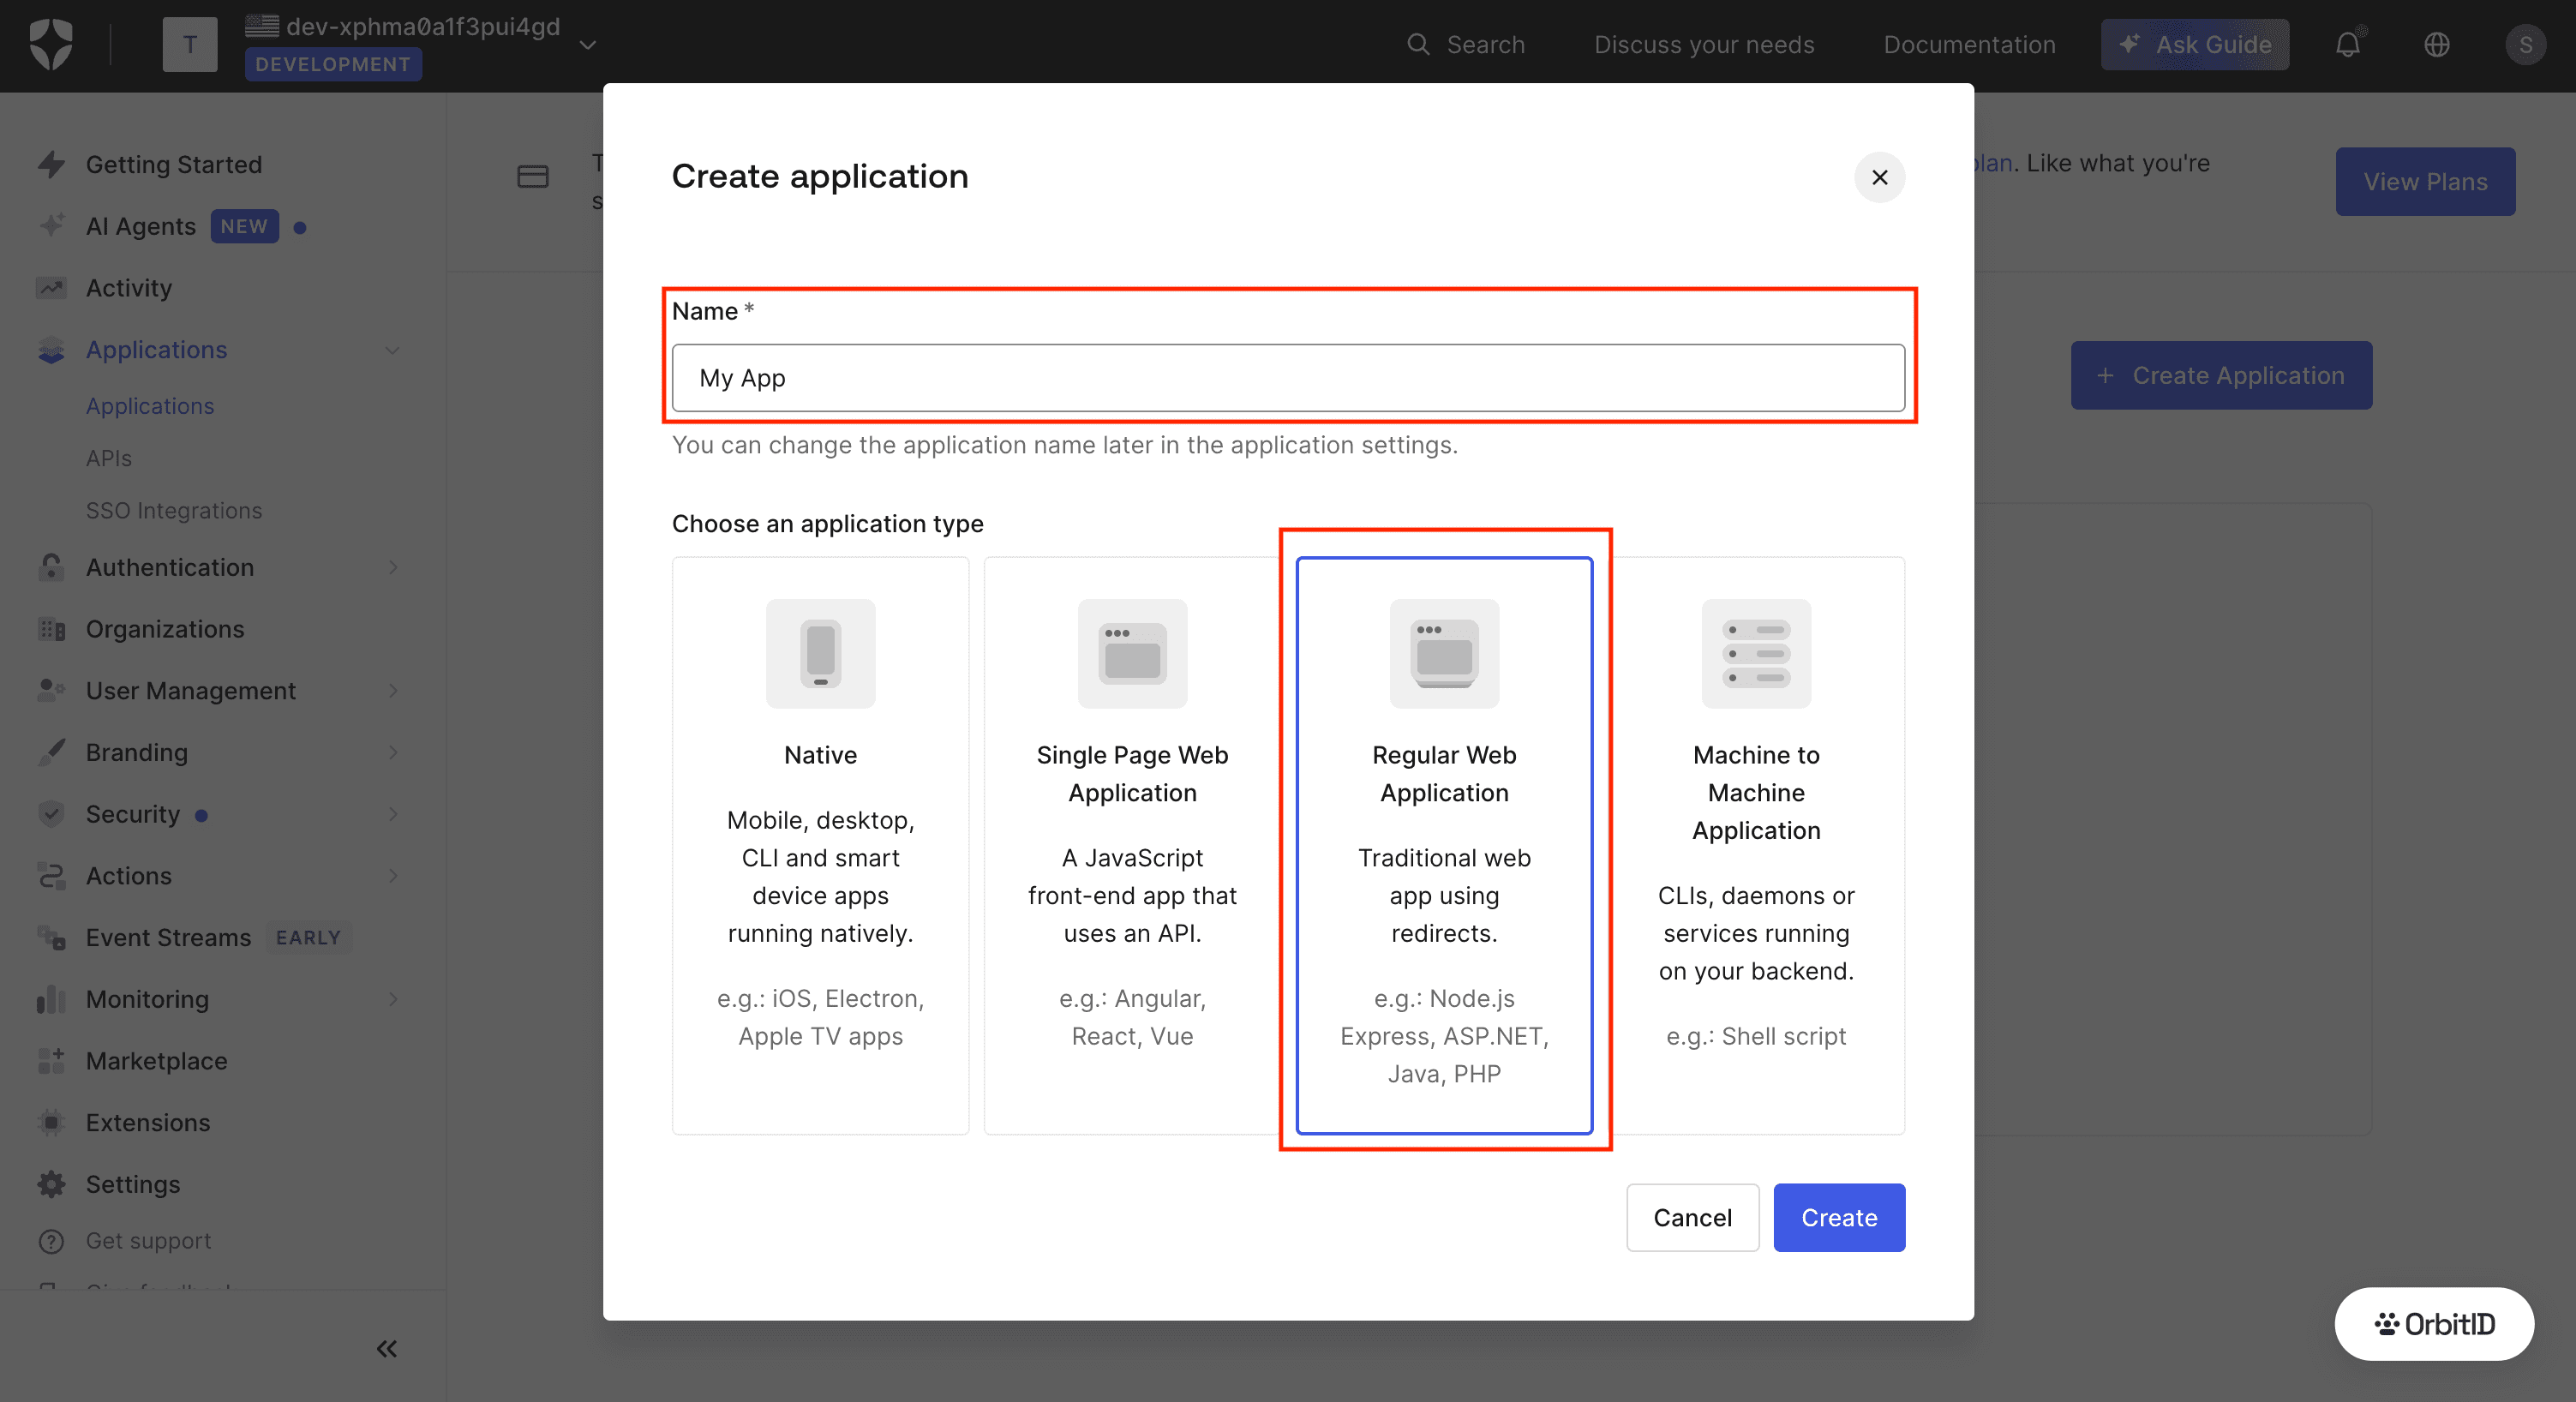
Give your application a Name and click Create.
Step 2: Configure application
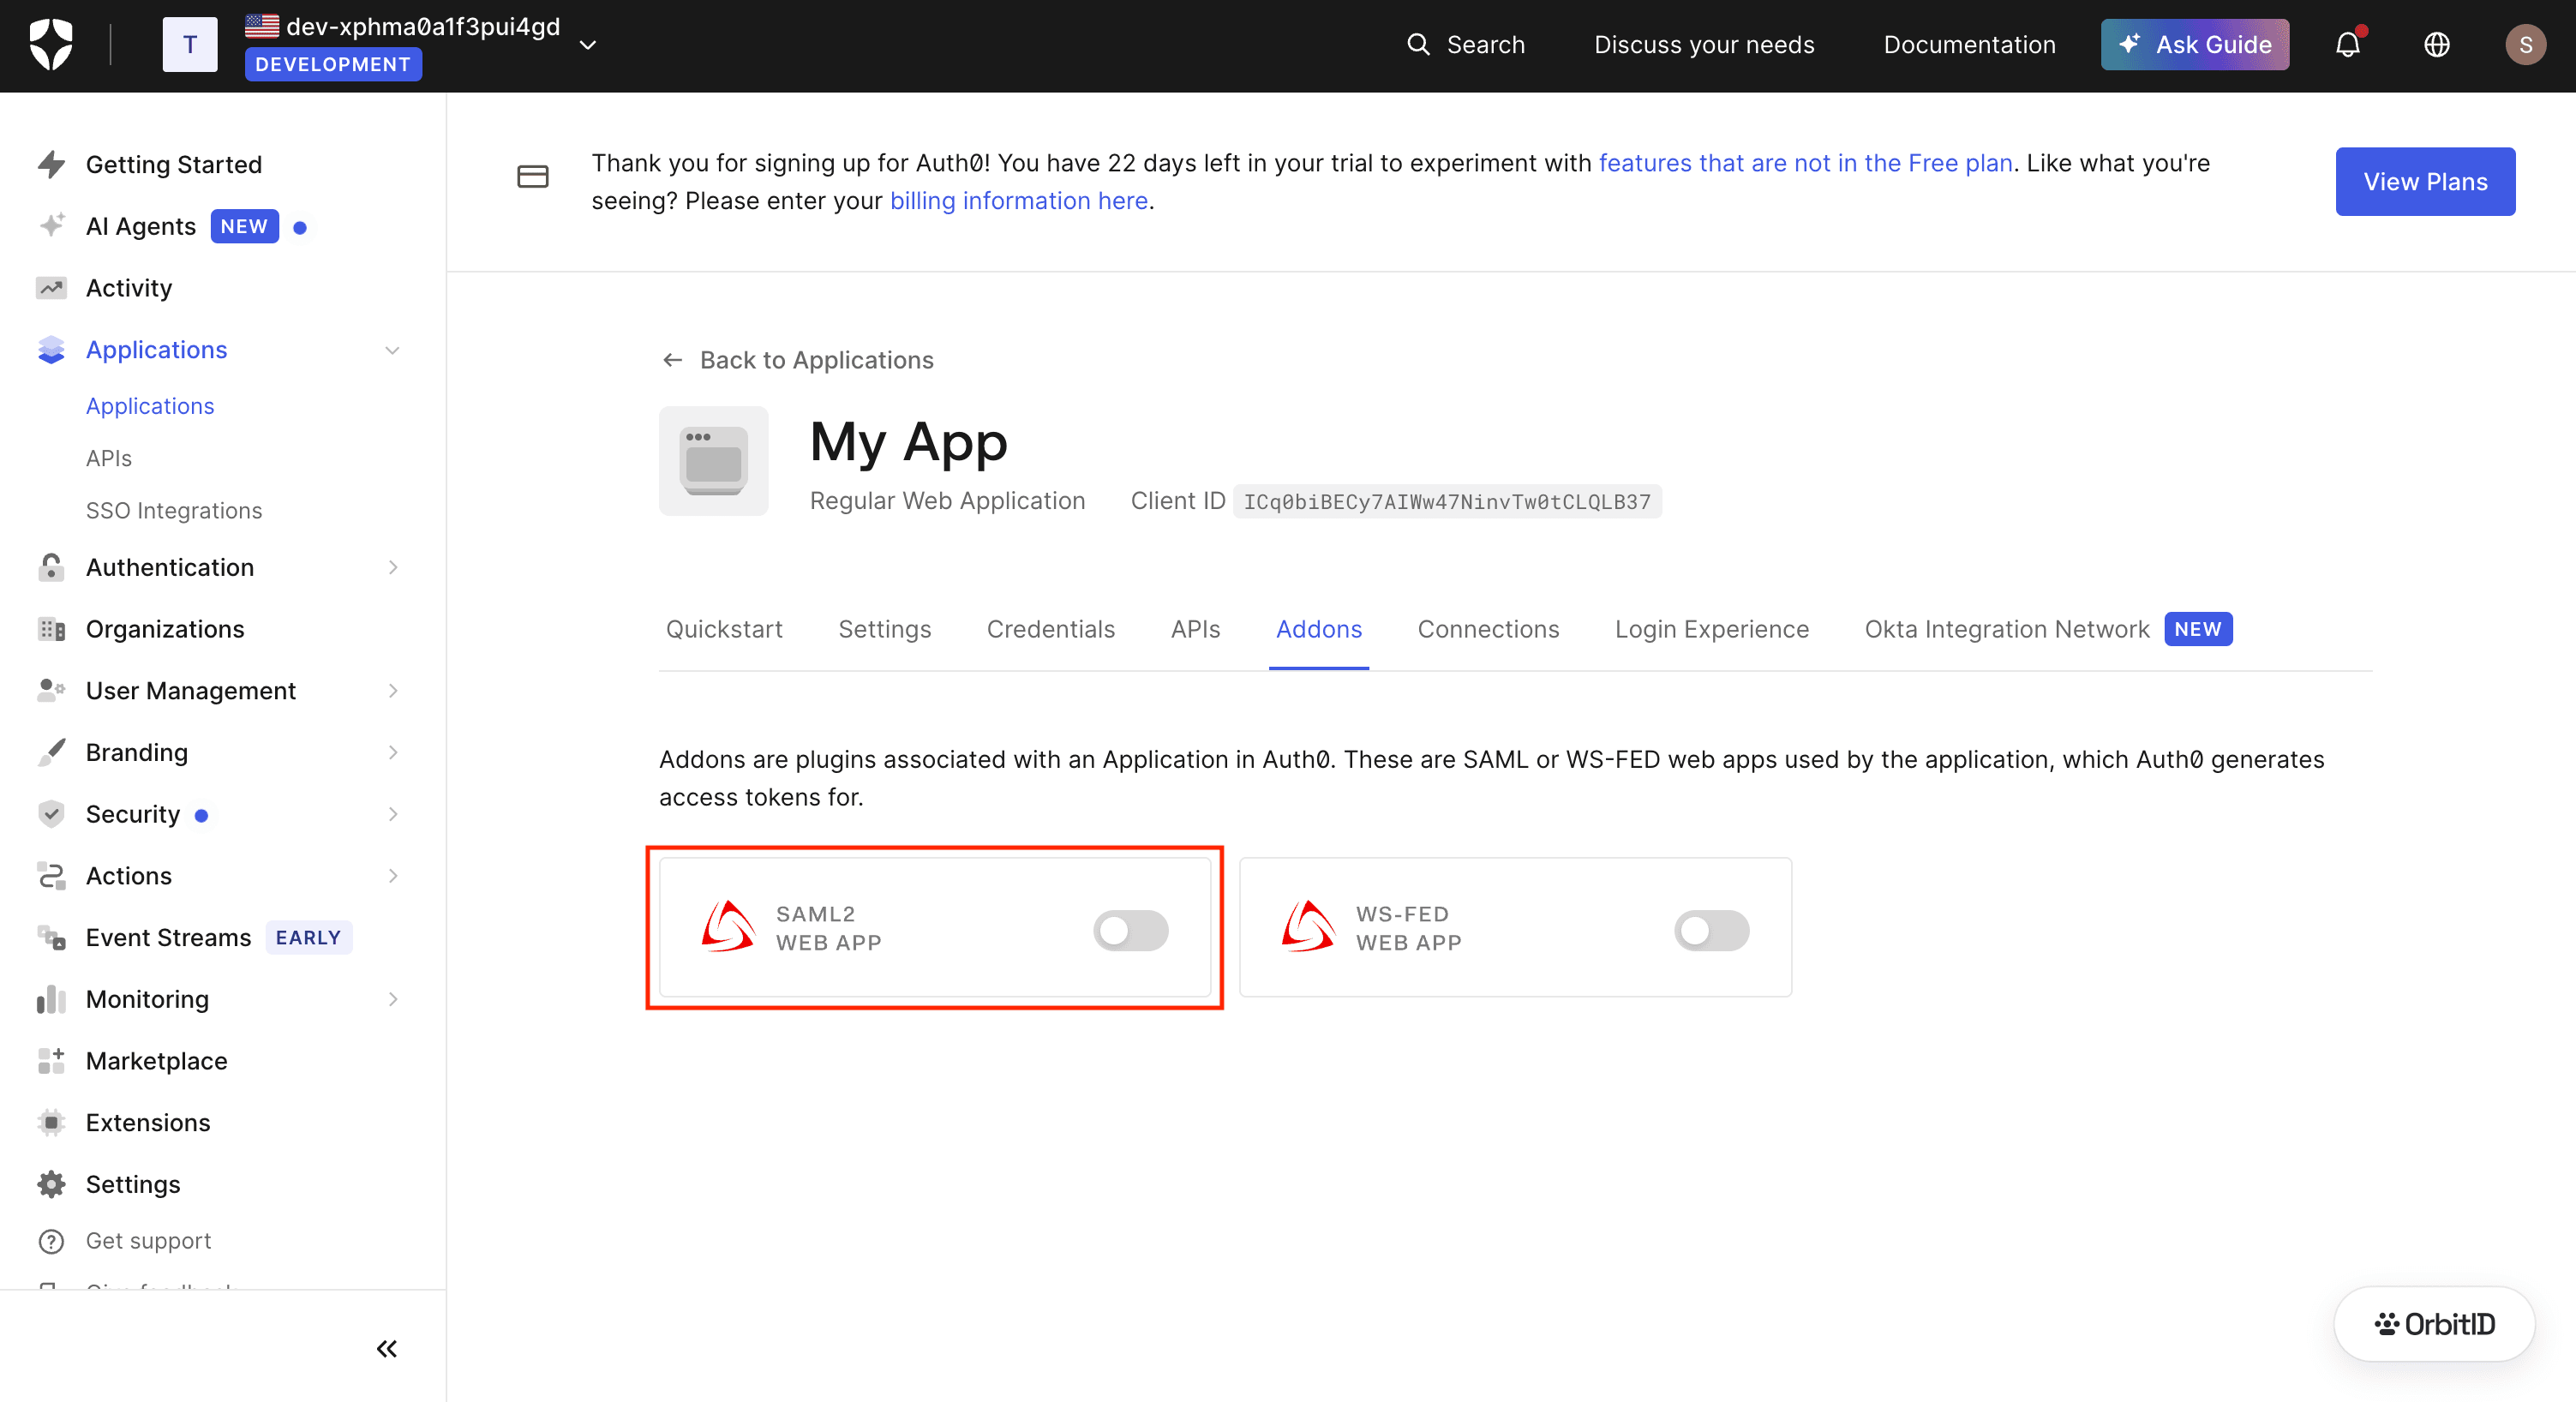
Click the tab Addons and enable the SAML2 WEB APP addon.
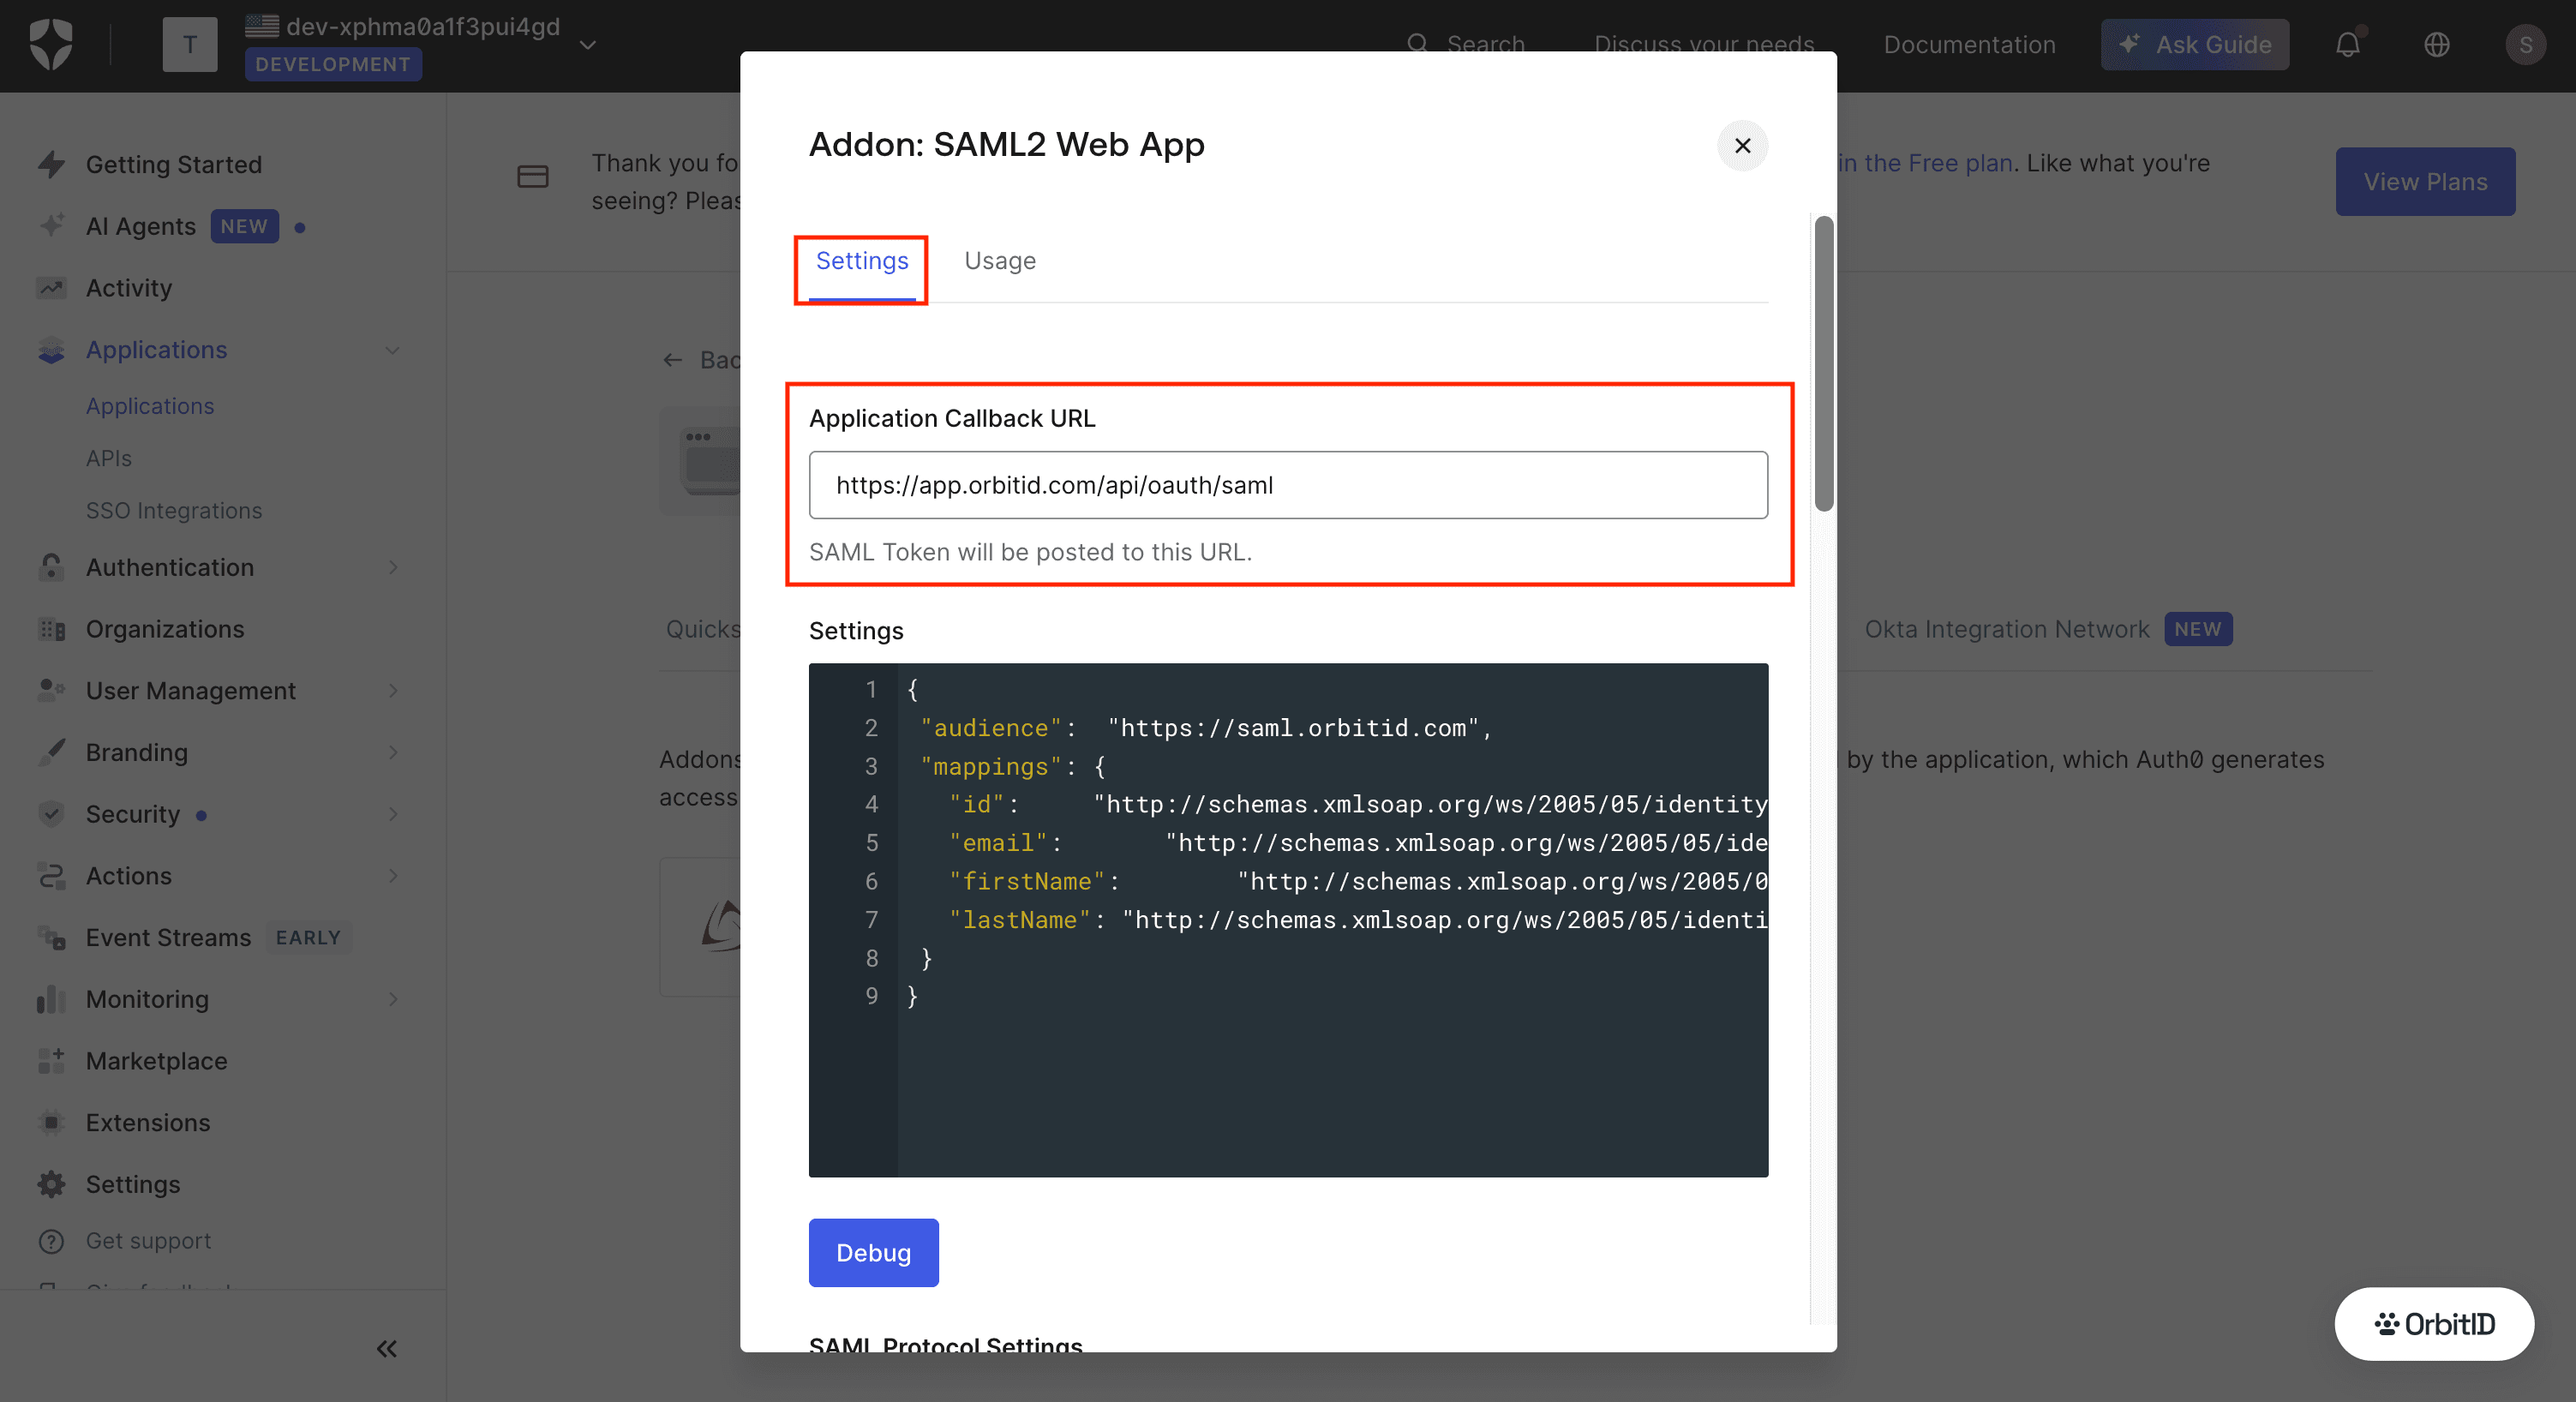
Enter your Application Callback URL on the next screen and click Enable.
- Application Callback URL
- https://app.orbitid.com/api/oauth/saml
- The ACS URL shown in your OrbitID Configuration page. Sandbox uses https://app.orbitid.com/api/oauth/sandbox/saml.
In the addon Settings, set "audience" to the SP Entity ID below and click Save. Without it, sign-ins that start from Auth0 carry an audience OrbitID rejects.
- Audience (SP Entity ID)
- https://saml.orbitid.com
- The SP Entity ID shown in your OrbitID Configuration page. Sandbox uses https://saml.orbitid.com/sandbox.
Auth0 sends email, given_name and family_name claims by default, which OrbitID maps to email, firstName and lastName; no extra attribute mapping is needed.
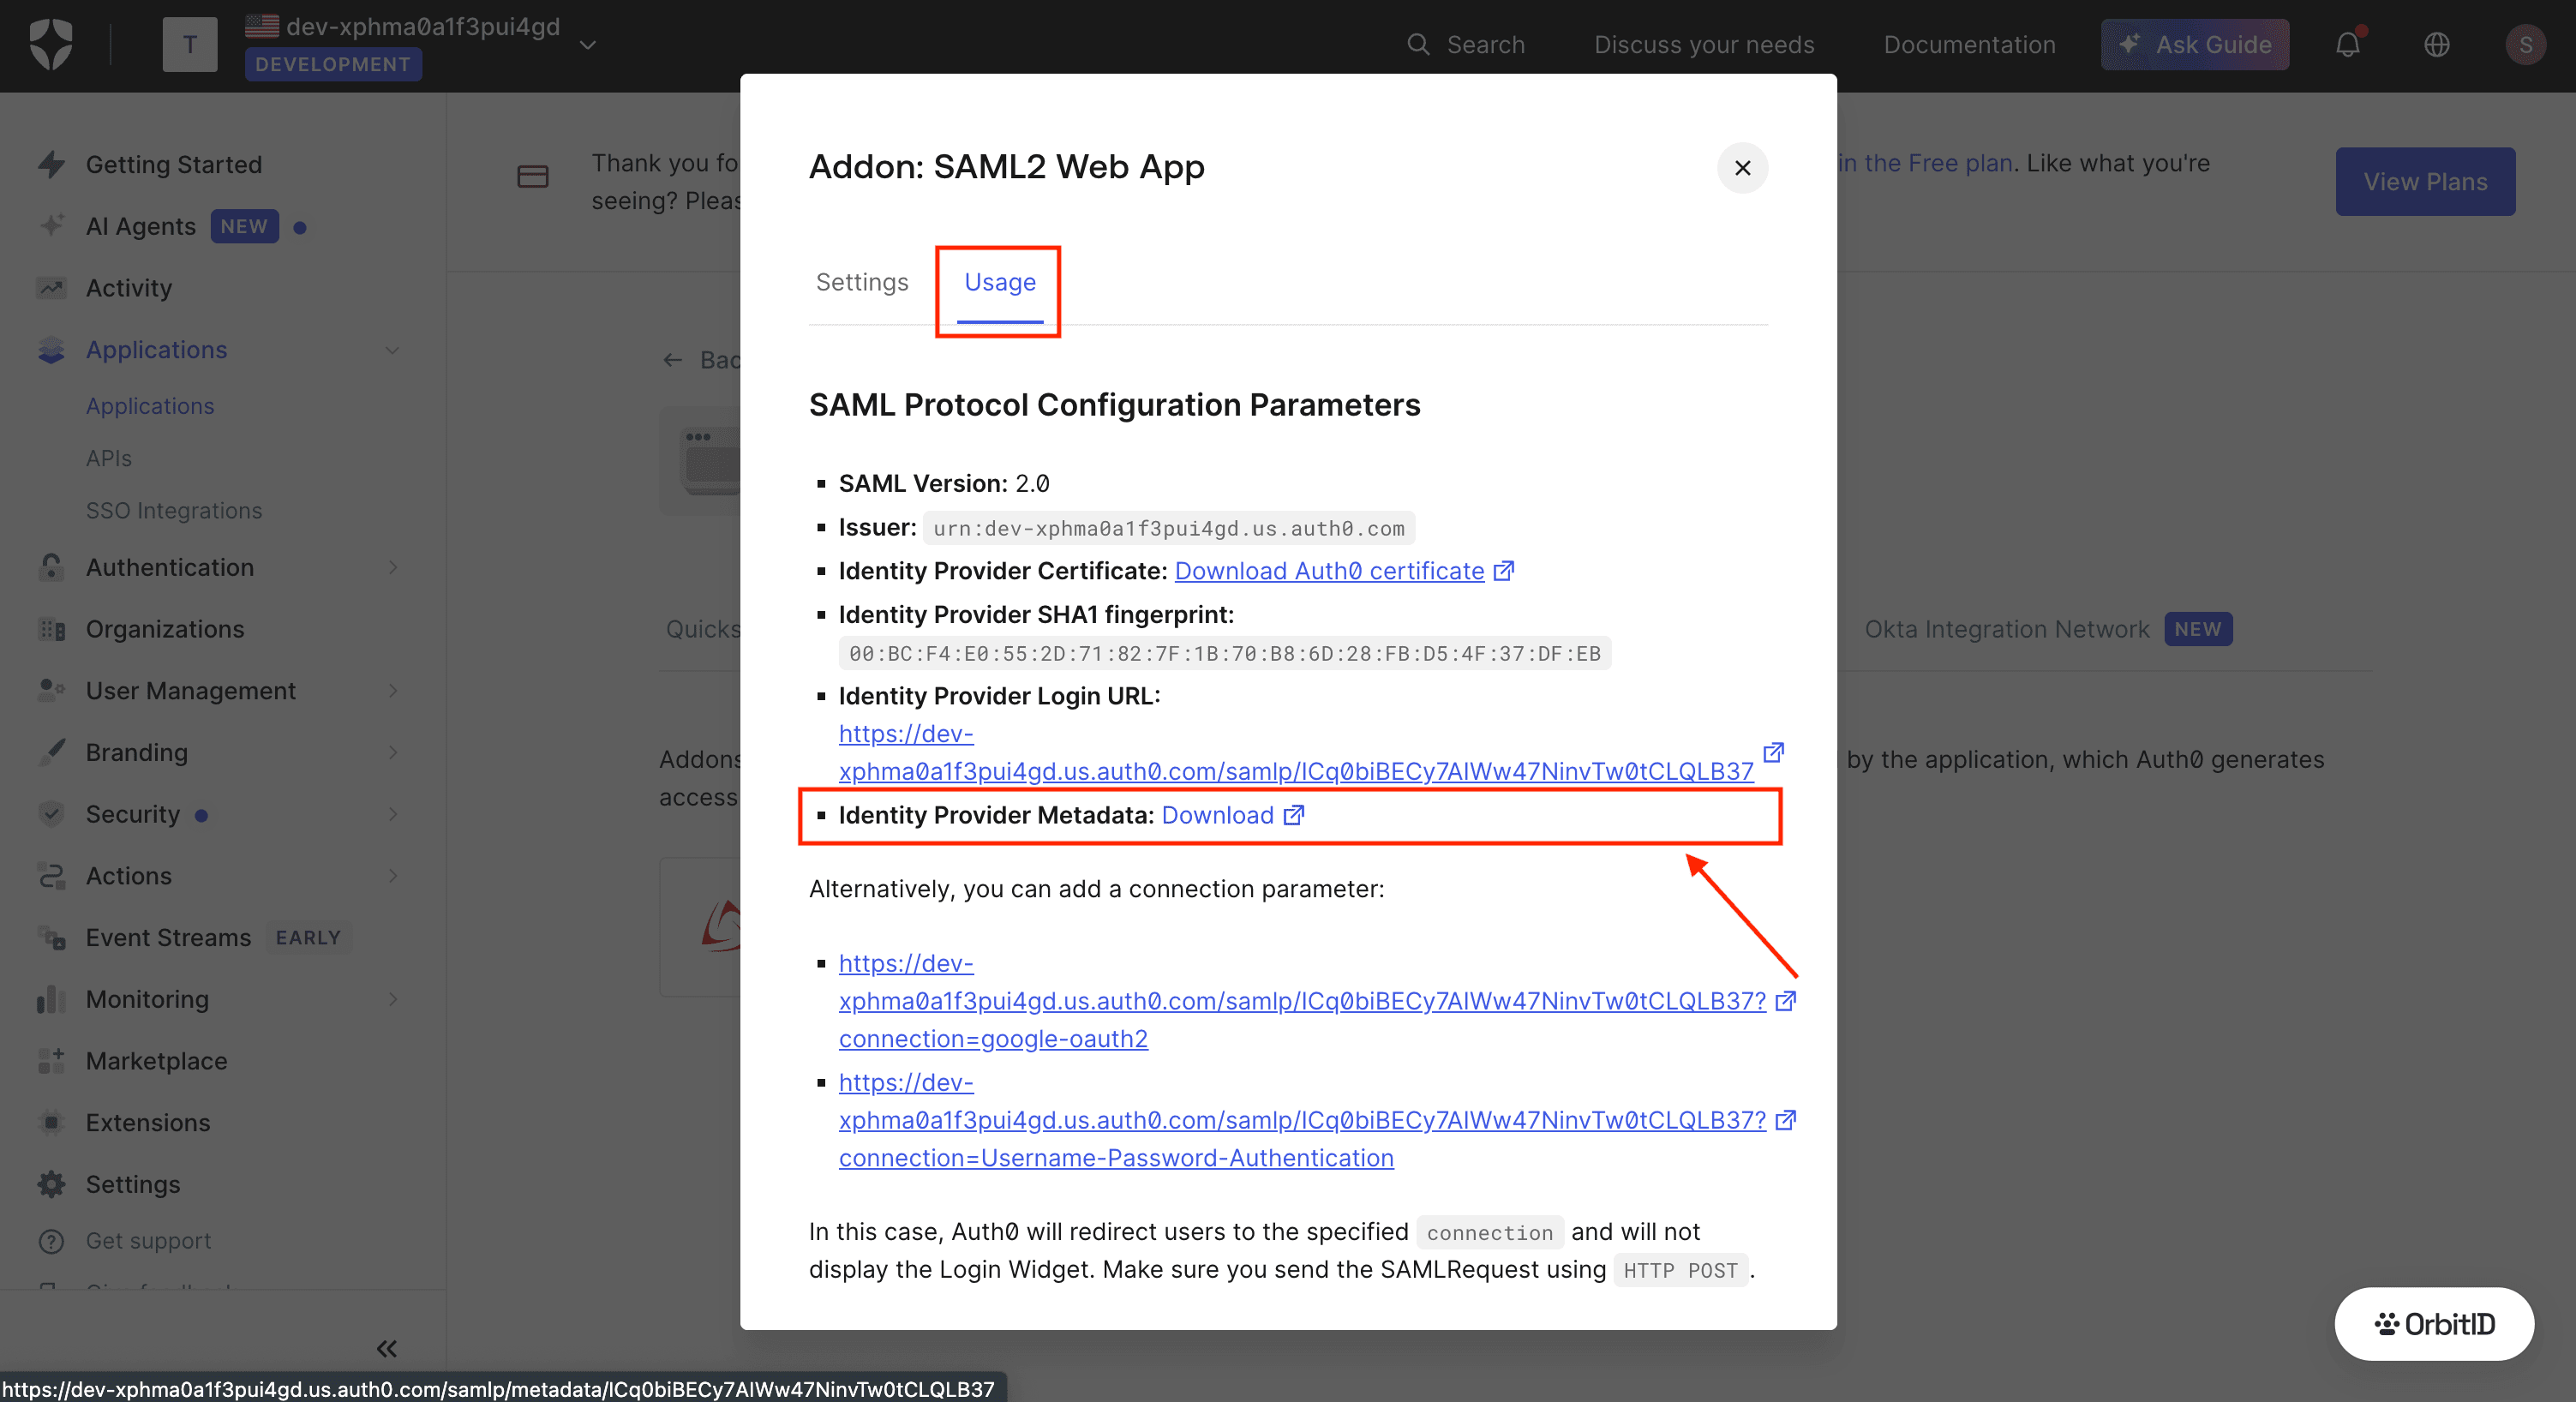
Step 3: Download the IdP metadata
Click the tab Usage and download the Identity Provider Metadata, or copy its URL.
Finish in OrbitID
Finish in OrbitID: paste the IdP metadata URL or XML into the connection form (or the Admin Portal link). In the dashboard, open the environment, go to Connections, click New connection, choose SAML and paste the metadata URL or the XML you downloaded. If your customer's admin is following an Admin Portal link, they paste it into the final step of the portal instead.
You can also create the connection with the API: POST /api/v1/sso as described in the quickstart.