Single sign-on · Setup guides
Microsoft Entra ID
Set up a SAML 2.0 enterprise application in Microsoft Entra ID (formerly Azure Active Directory) and connect it to OrbitID. You need an Entra ID administrator account.
Step 1: Create application
From your Azure admin console, click Enterprise applications from the left navigation menu.
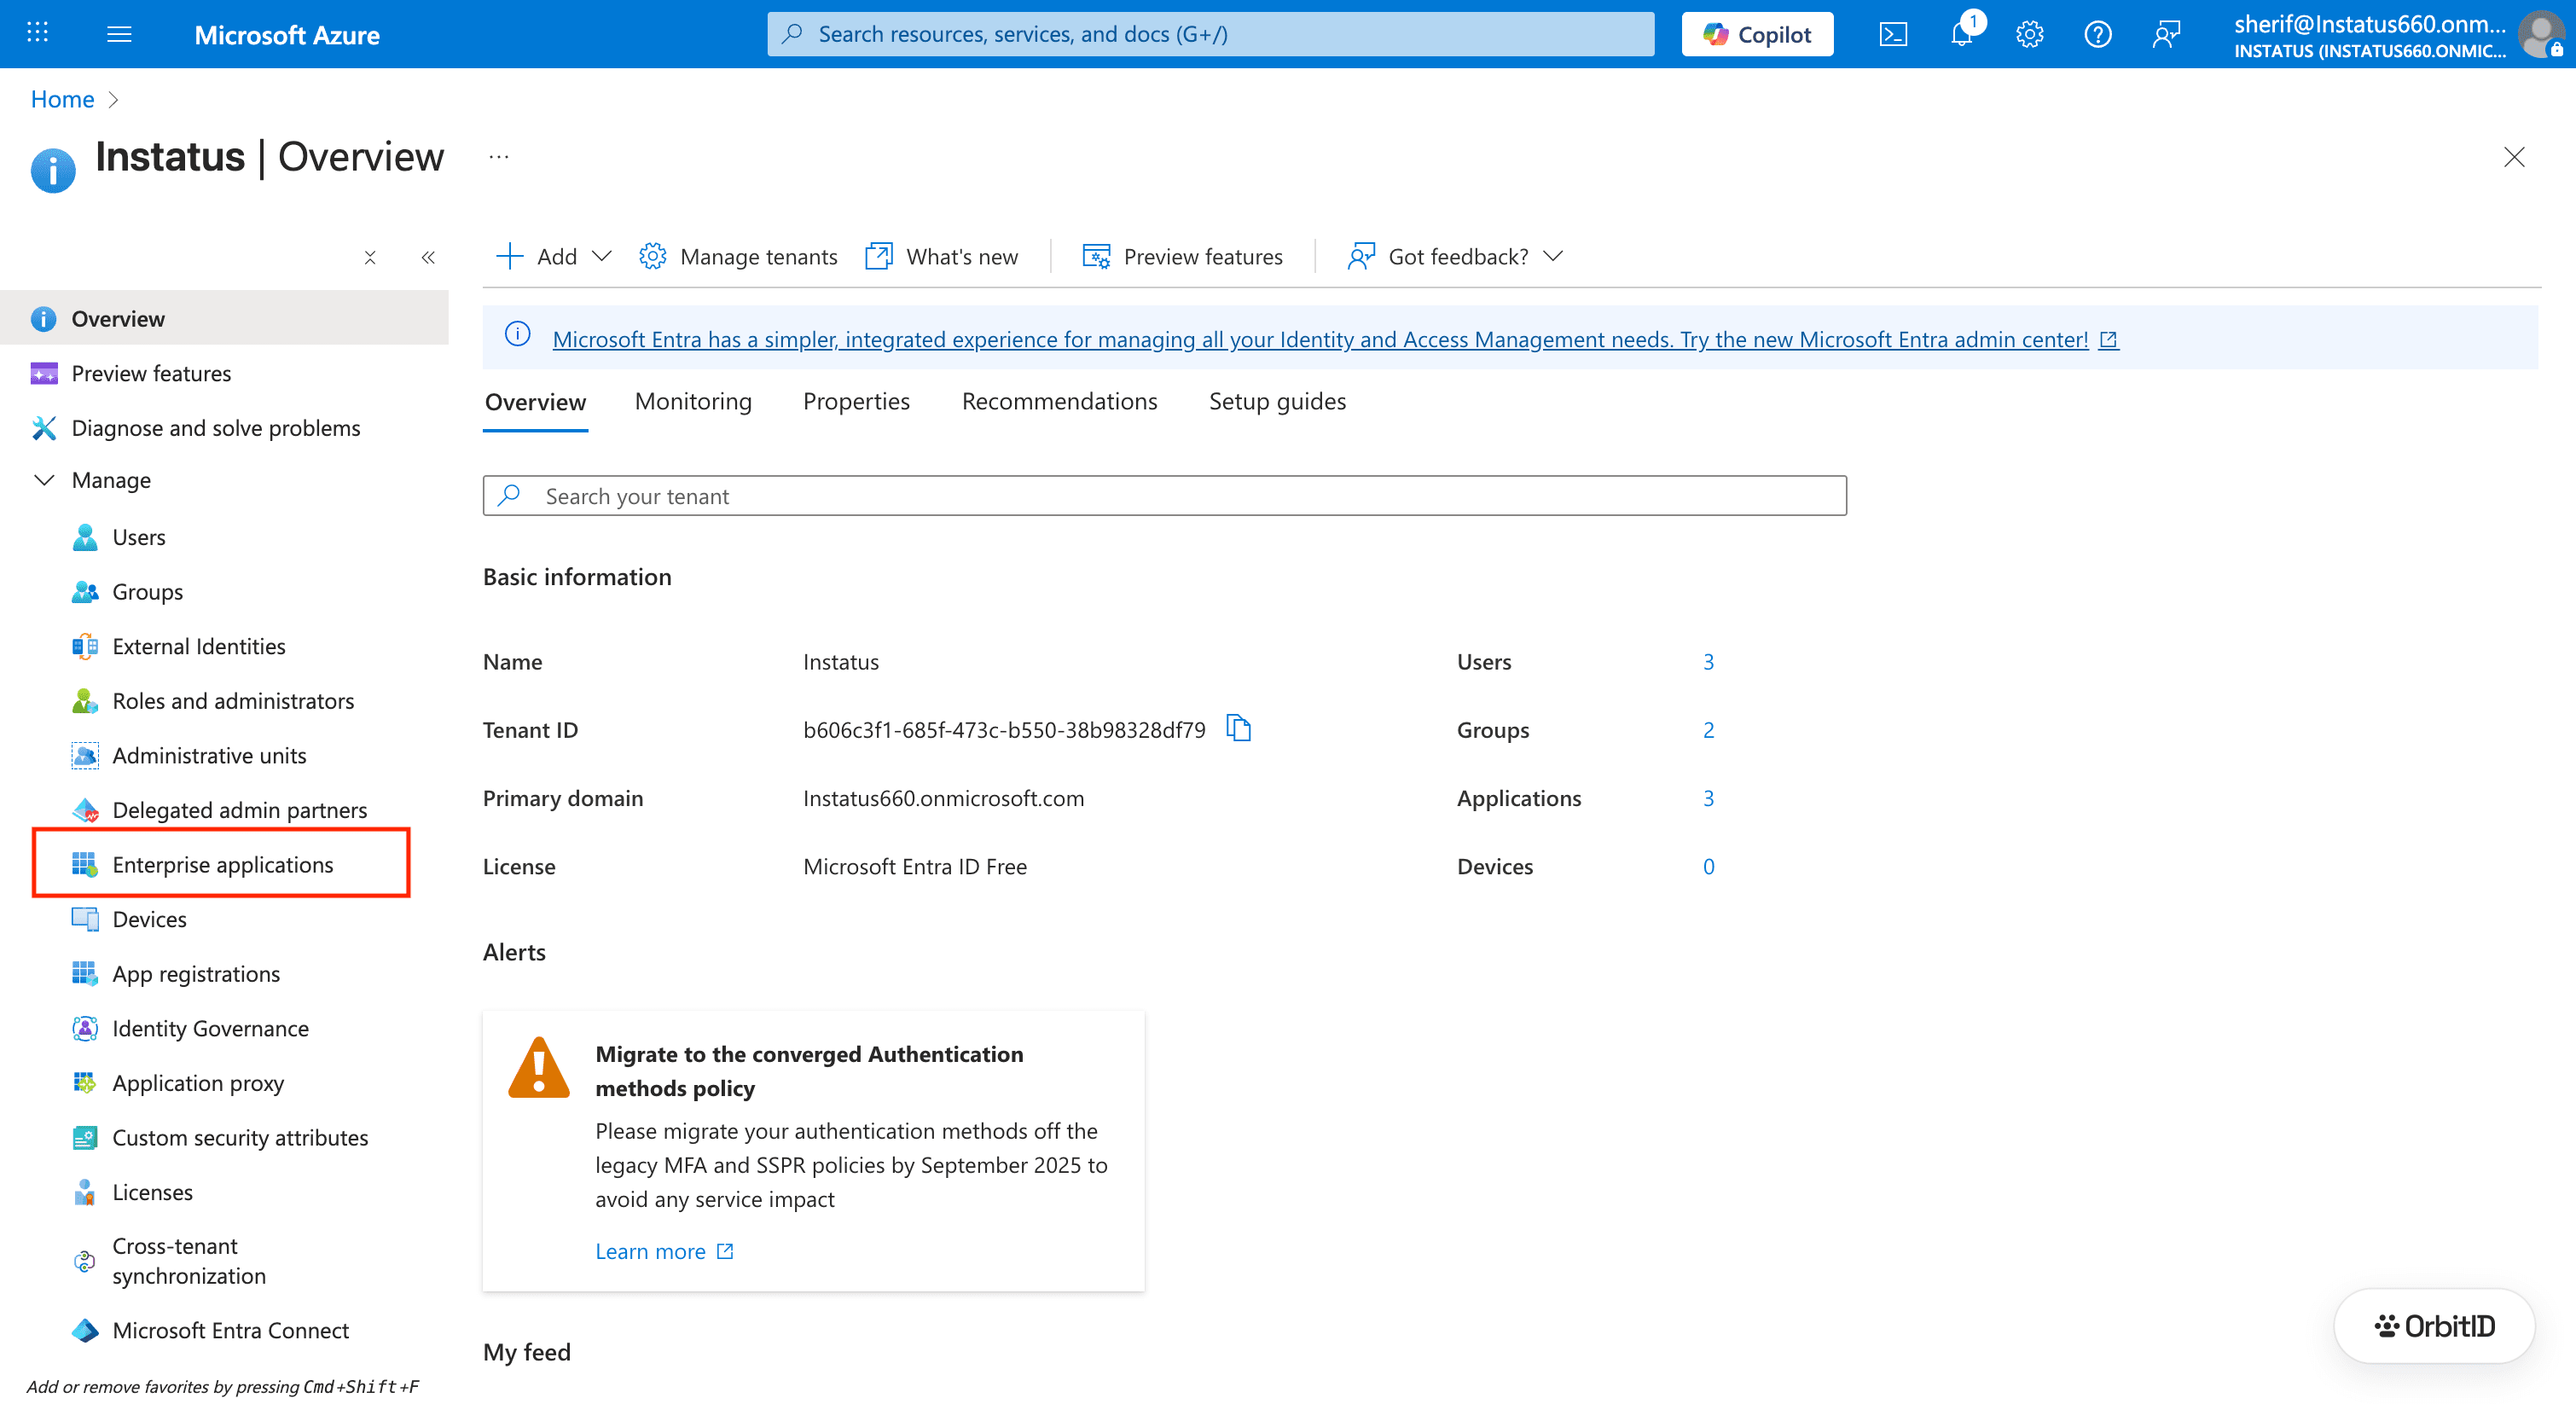
If your application is already created, choose it from the list and move to the next step.
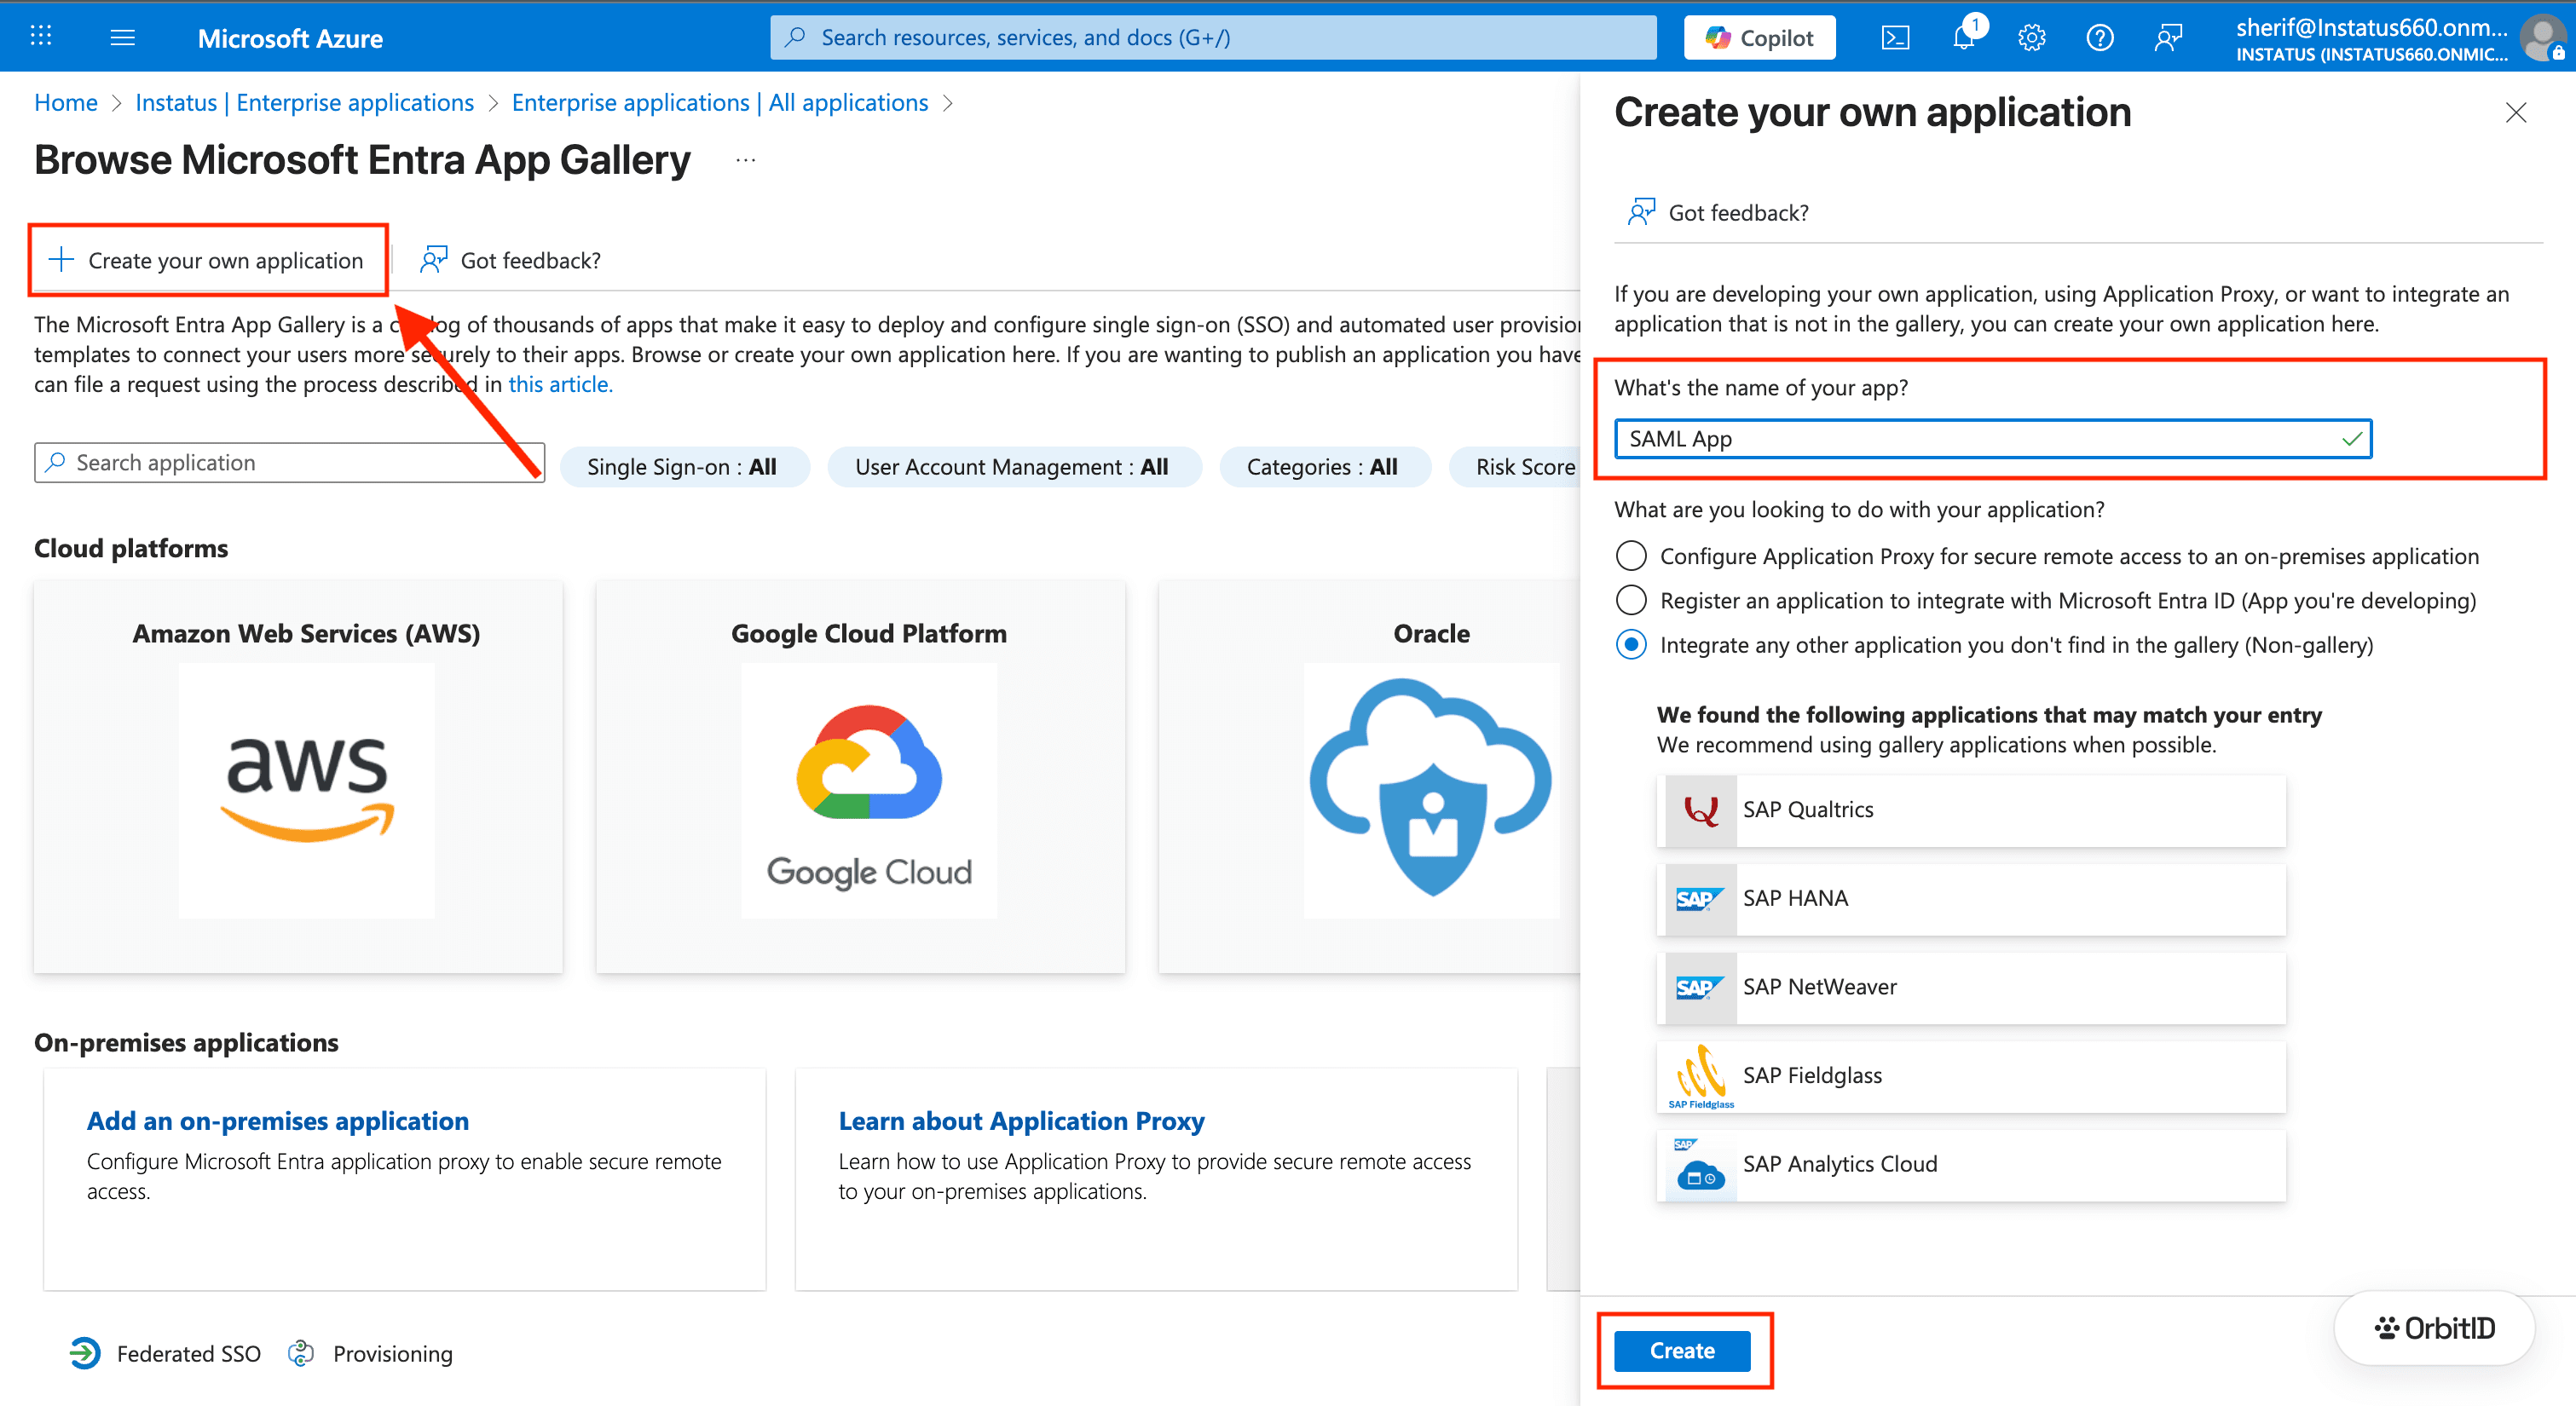
If you haven't created a SAML application, click New application from the top to create a new application.
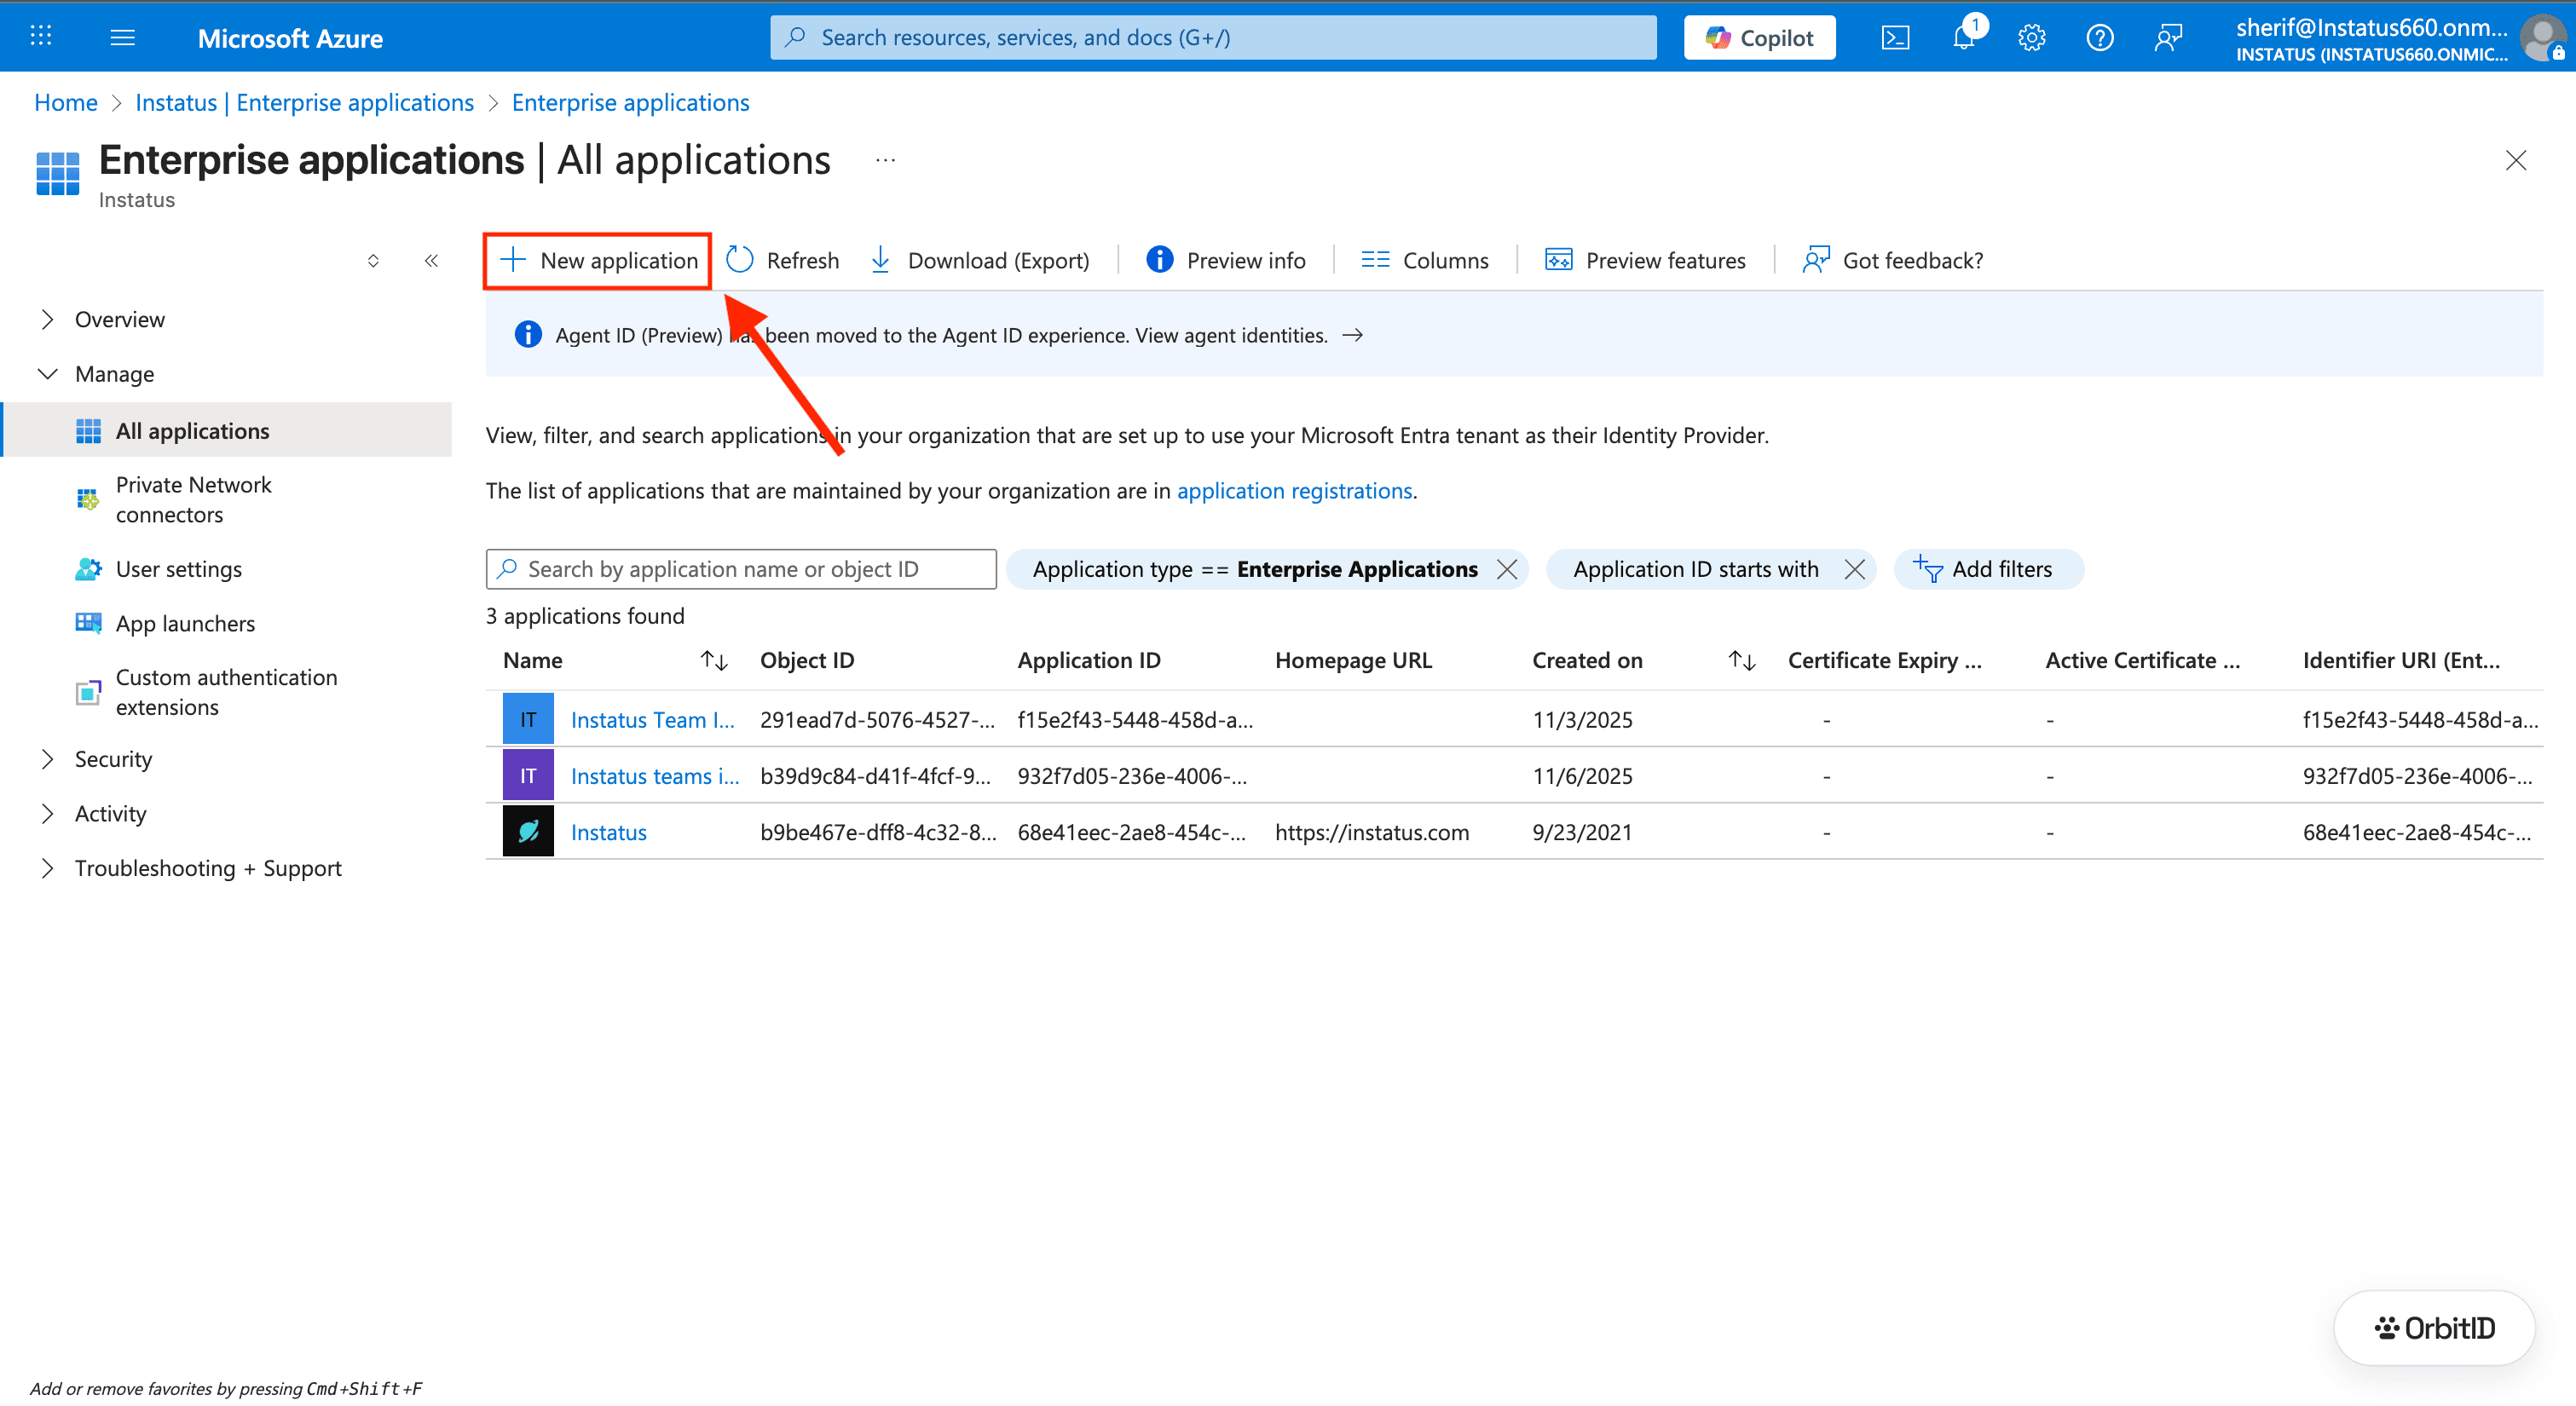
From the next screen, click Create your own application.
Give your application a Name and click Create.
Step 2: Configure application
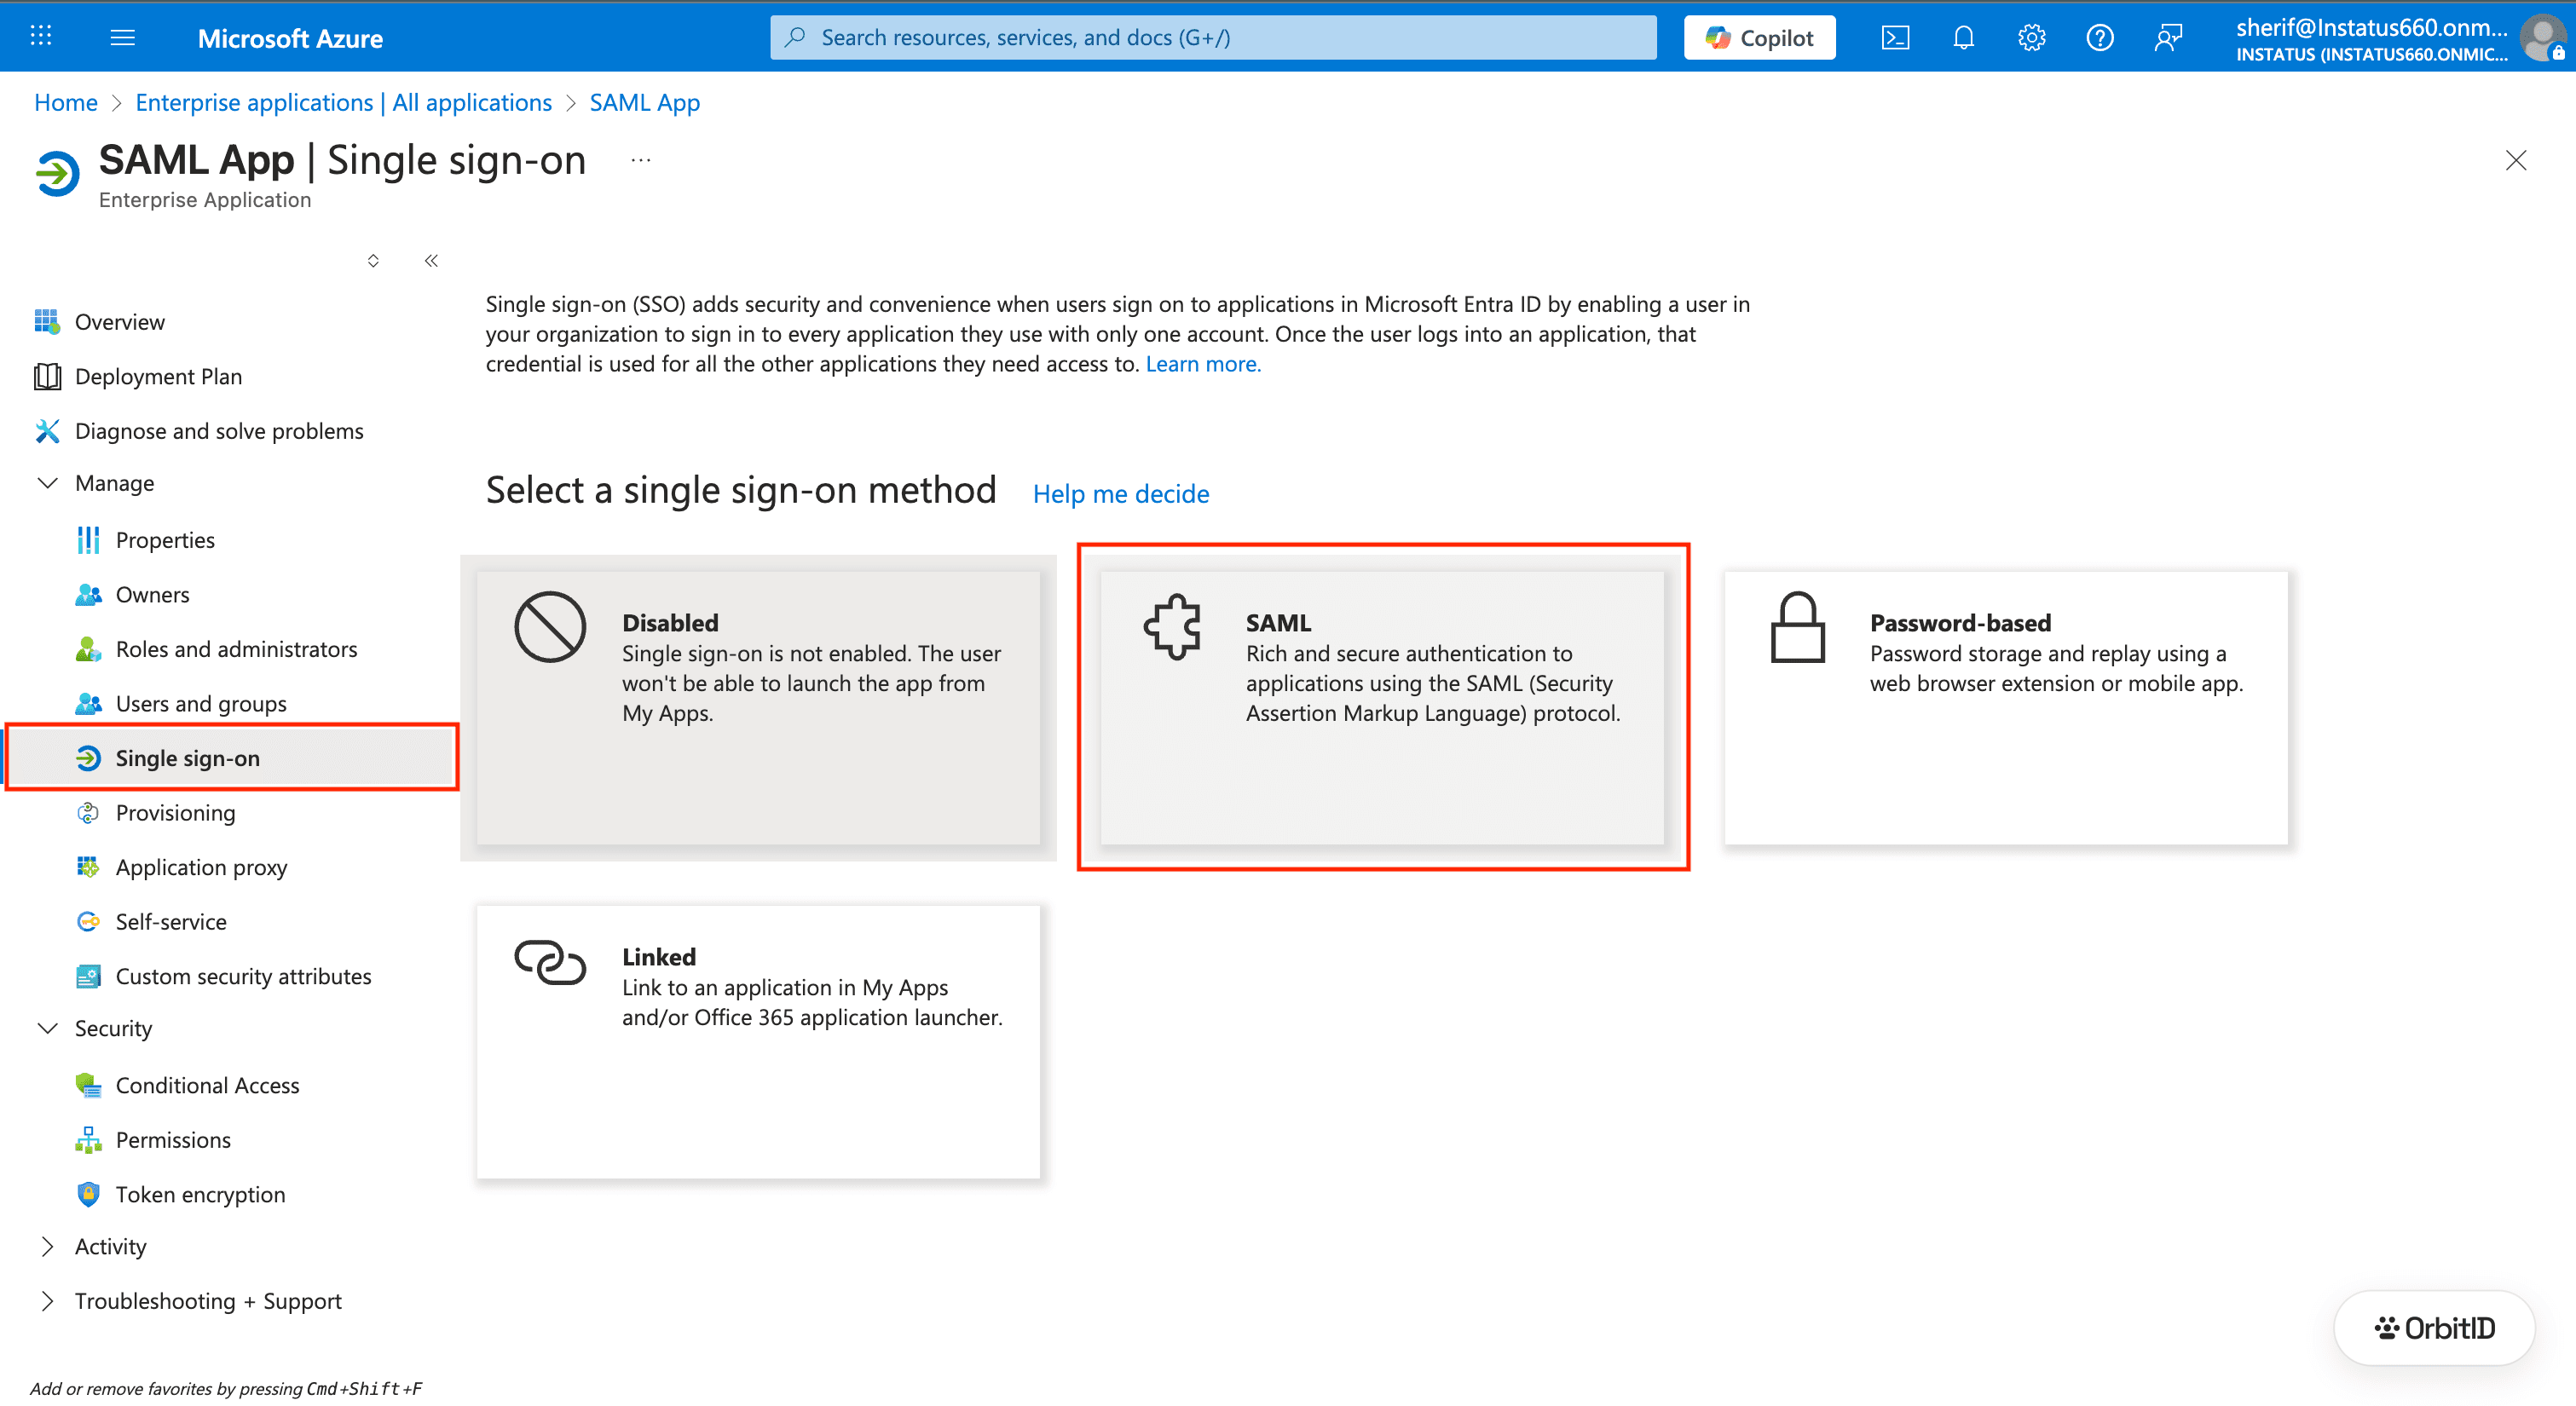
Select Single Sign On from the Manage section of your app and then SAML.
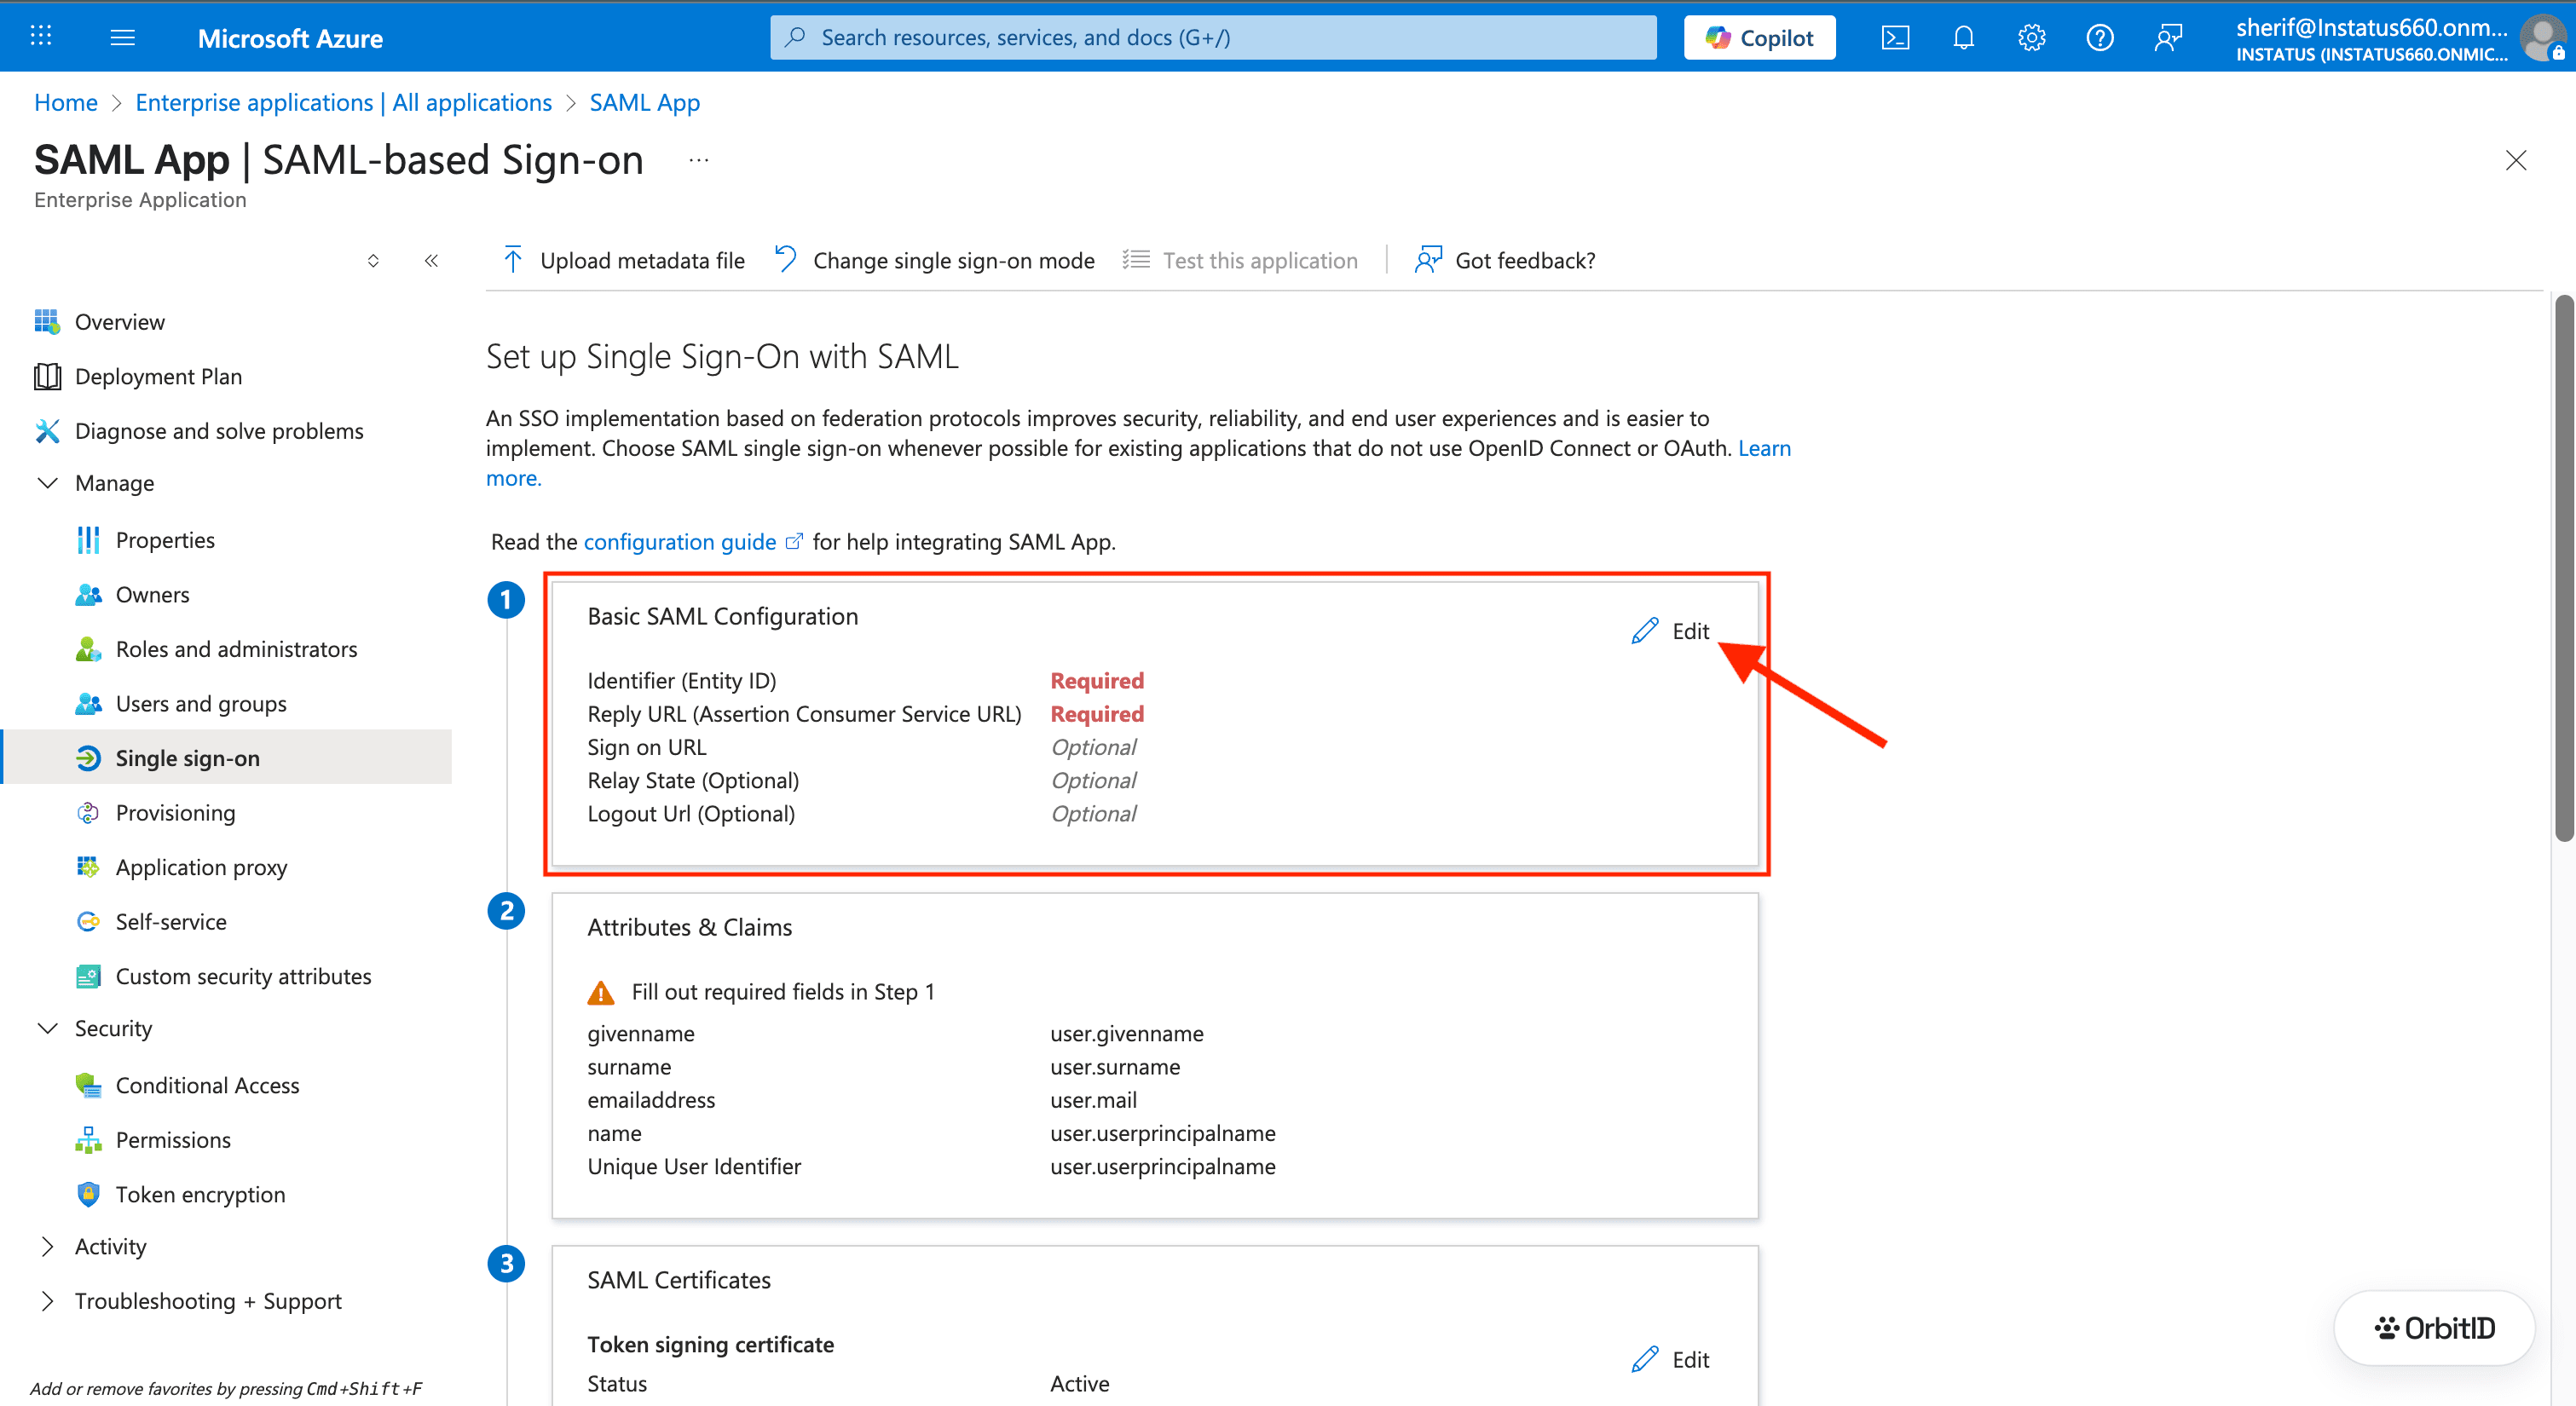
Click Edit on the Basic SAML Configuration section.
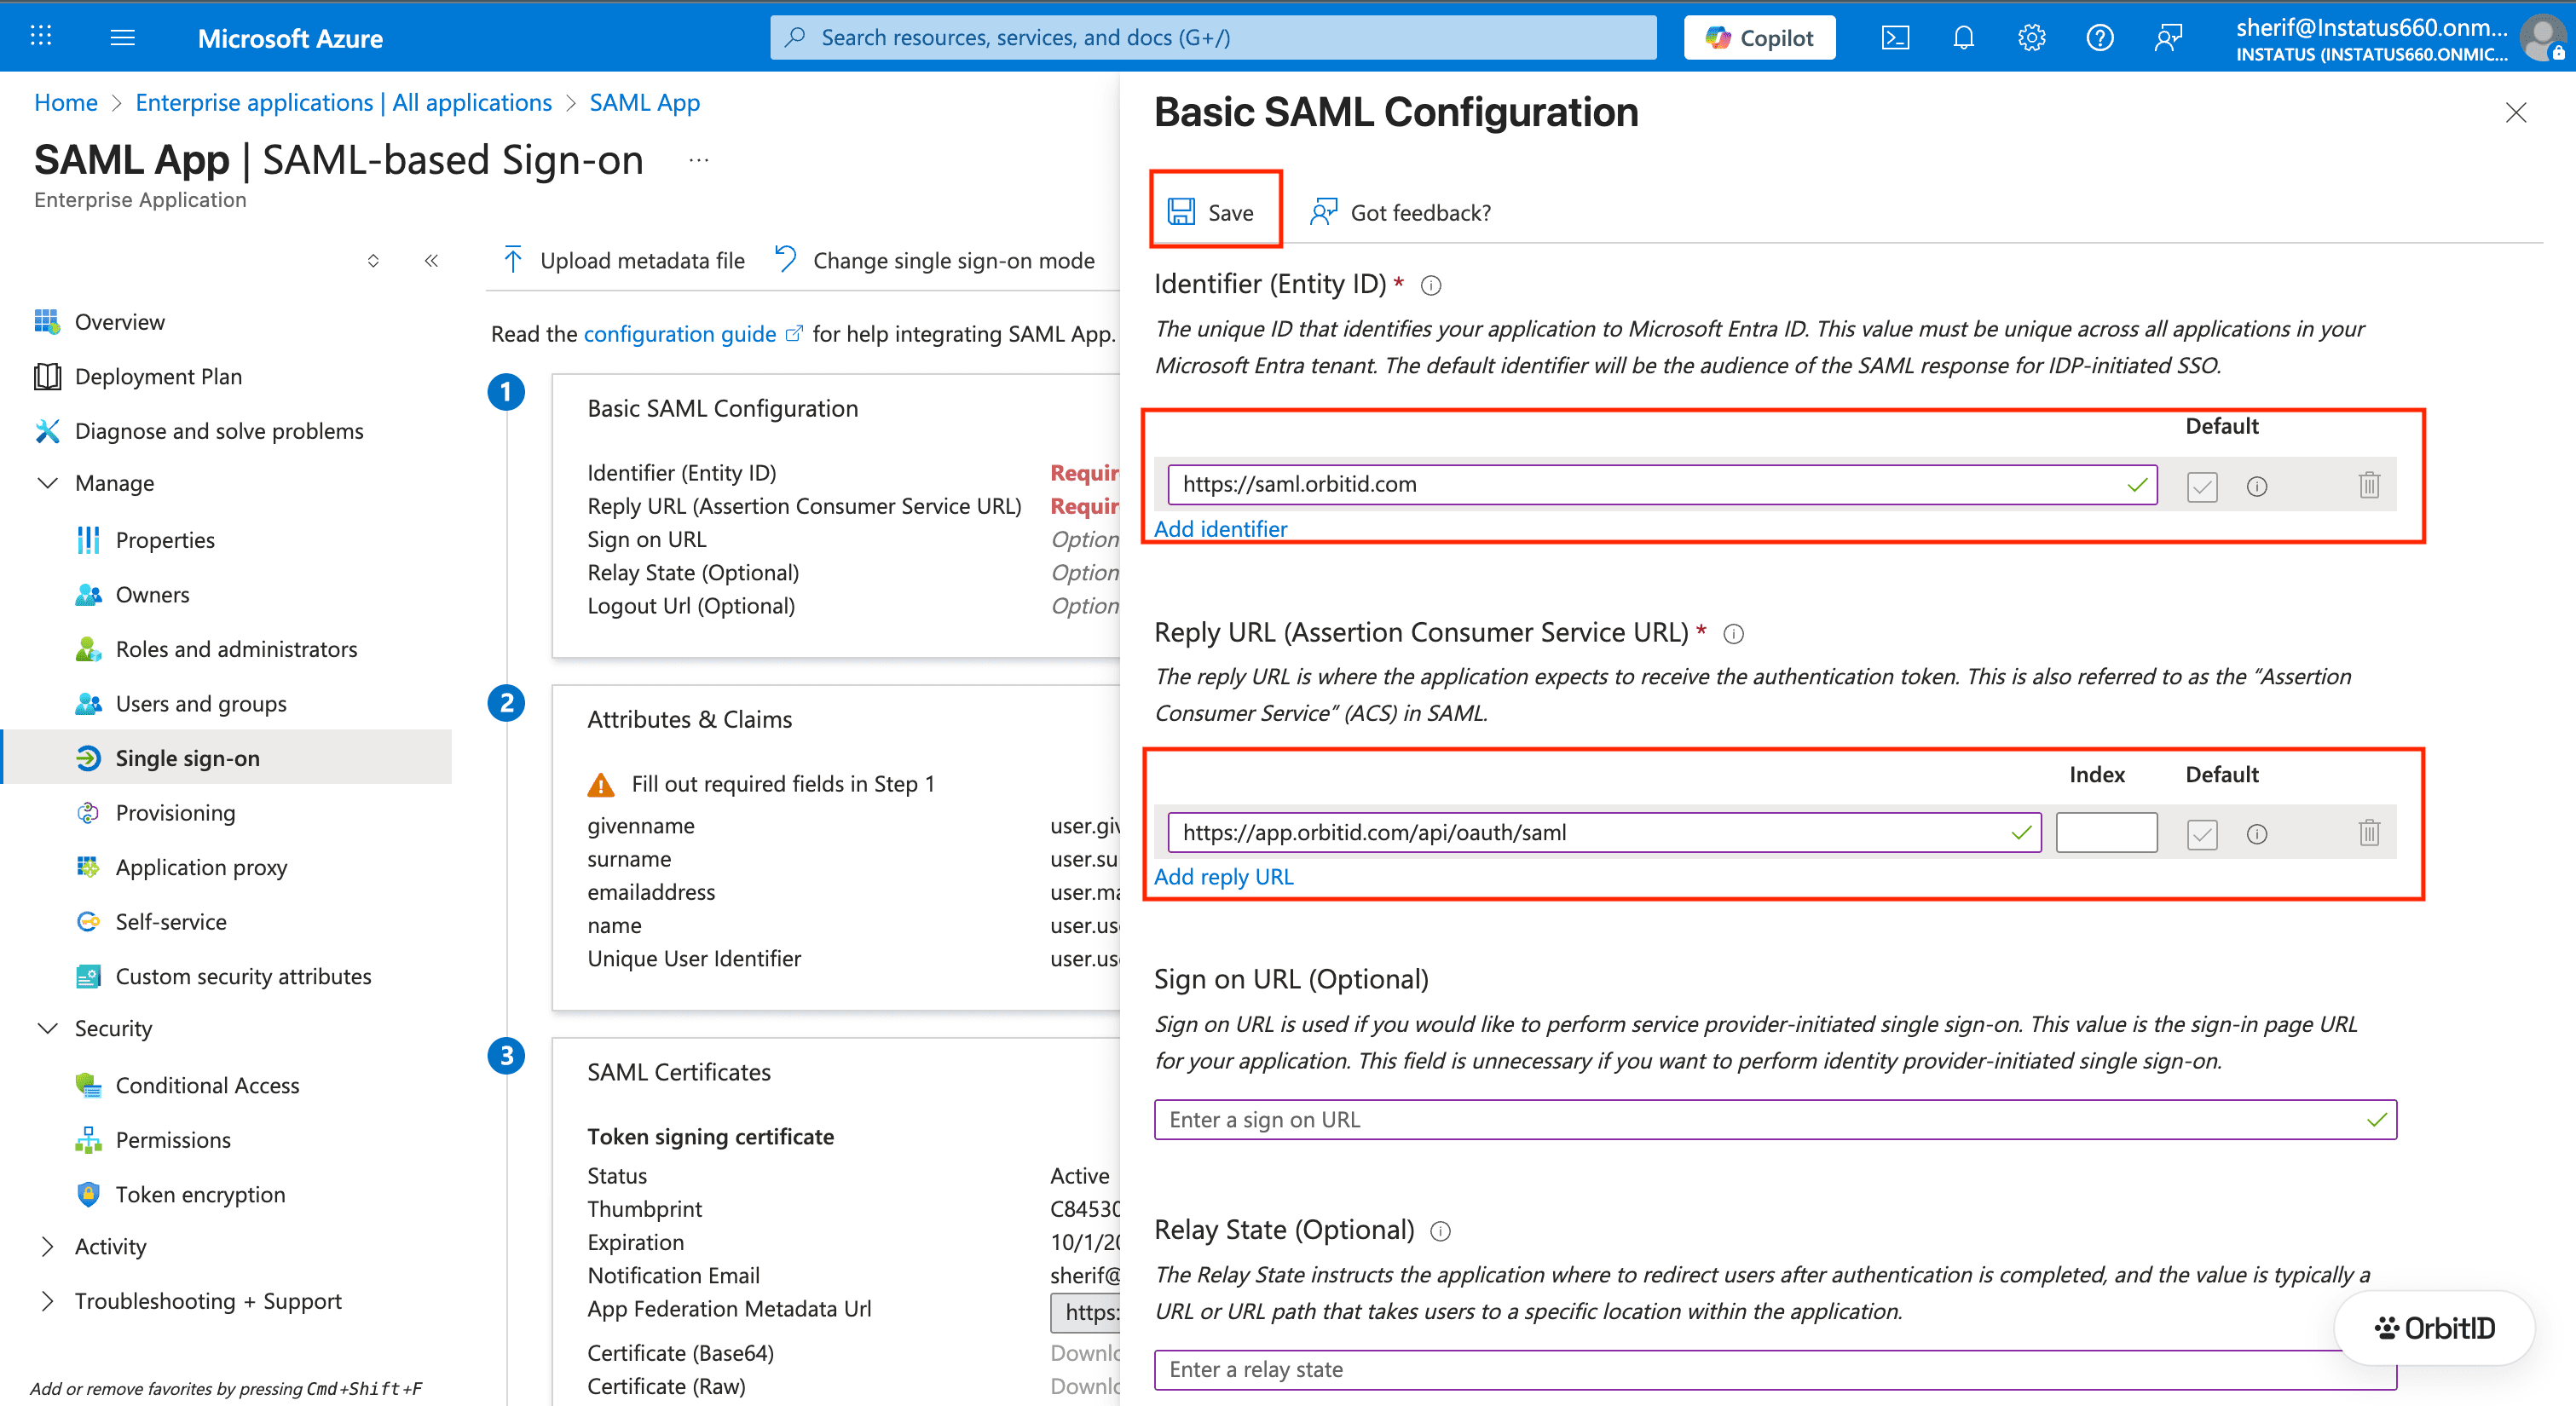
Enter the following values in the Basic SAML Configuration section on the next screen:
- Reply URL (Assertion Consumer Service URL)
- https://app.orbitid.com/api/oauth/saml
- The ACS URL shown in your OrbitID Configuration page. Sandbox uses https://app.orbitid.com/api/oauth/sandbox/saml.
- Identifier (Entity ID)
- https://saml.orbitid.com
- The SP Entity ID shown in your OrbitID Configuration page. Sandbox uses https://saml.orbitid.com/sandbox.
Click Save to save your changes.
Step 3: Attribute mapping
Click Edit on the Attributes & Claims section.
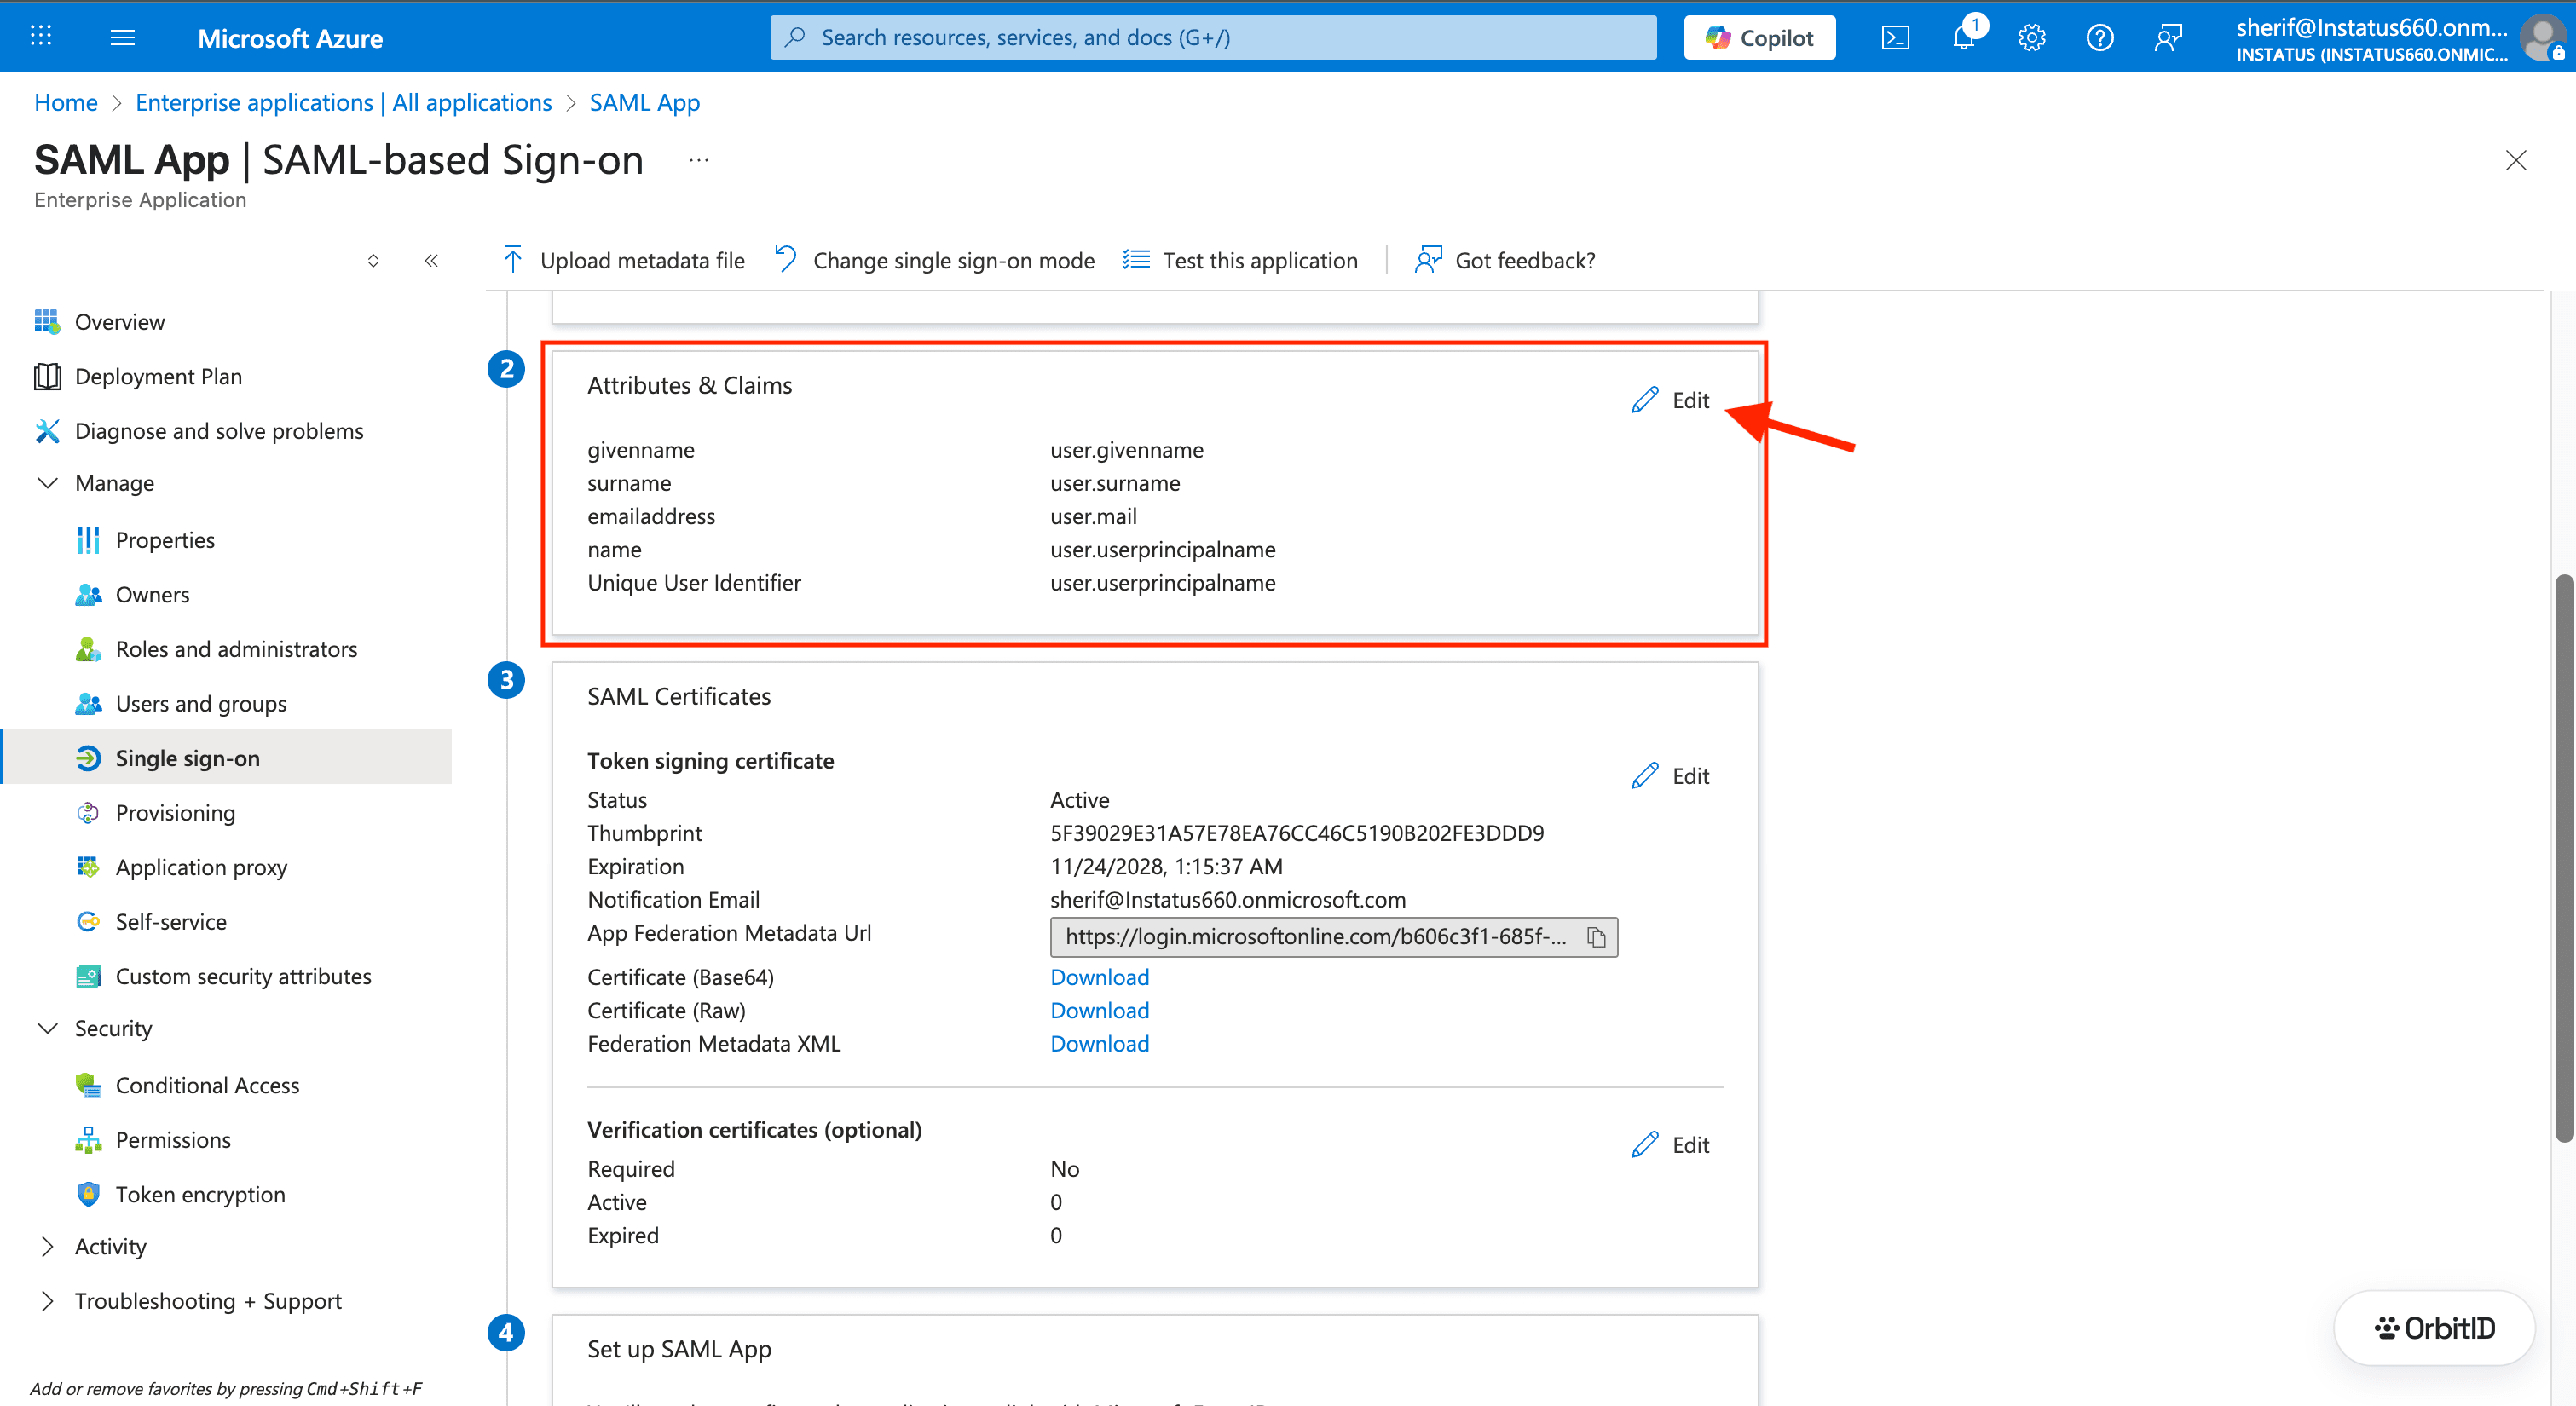
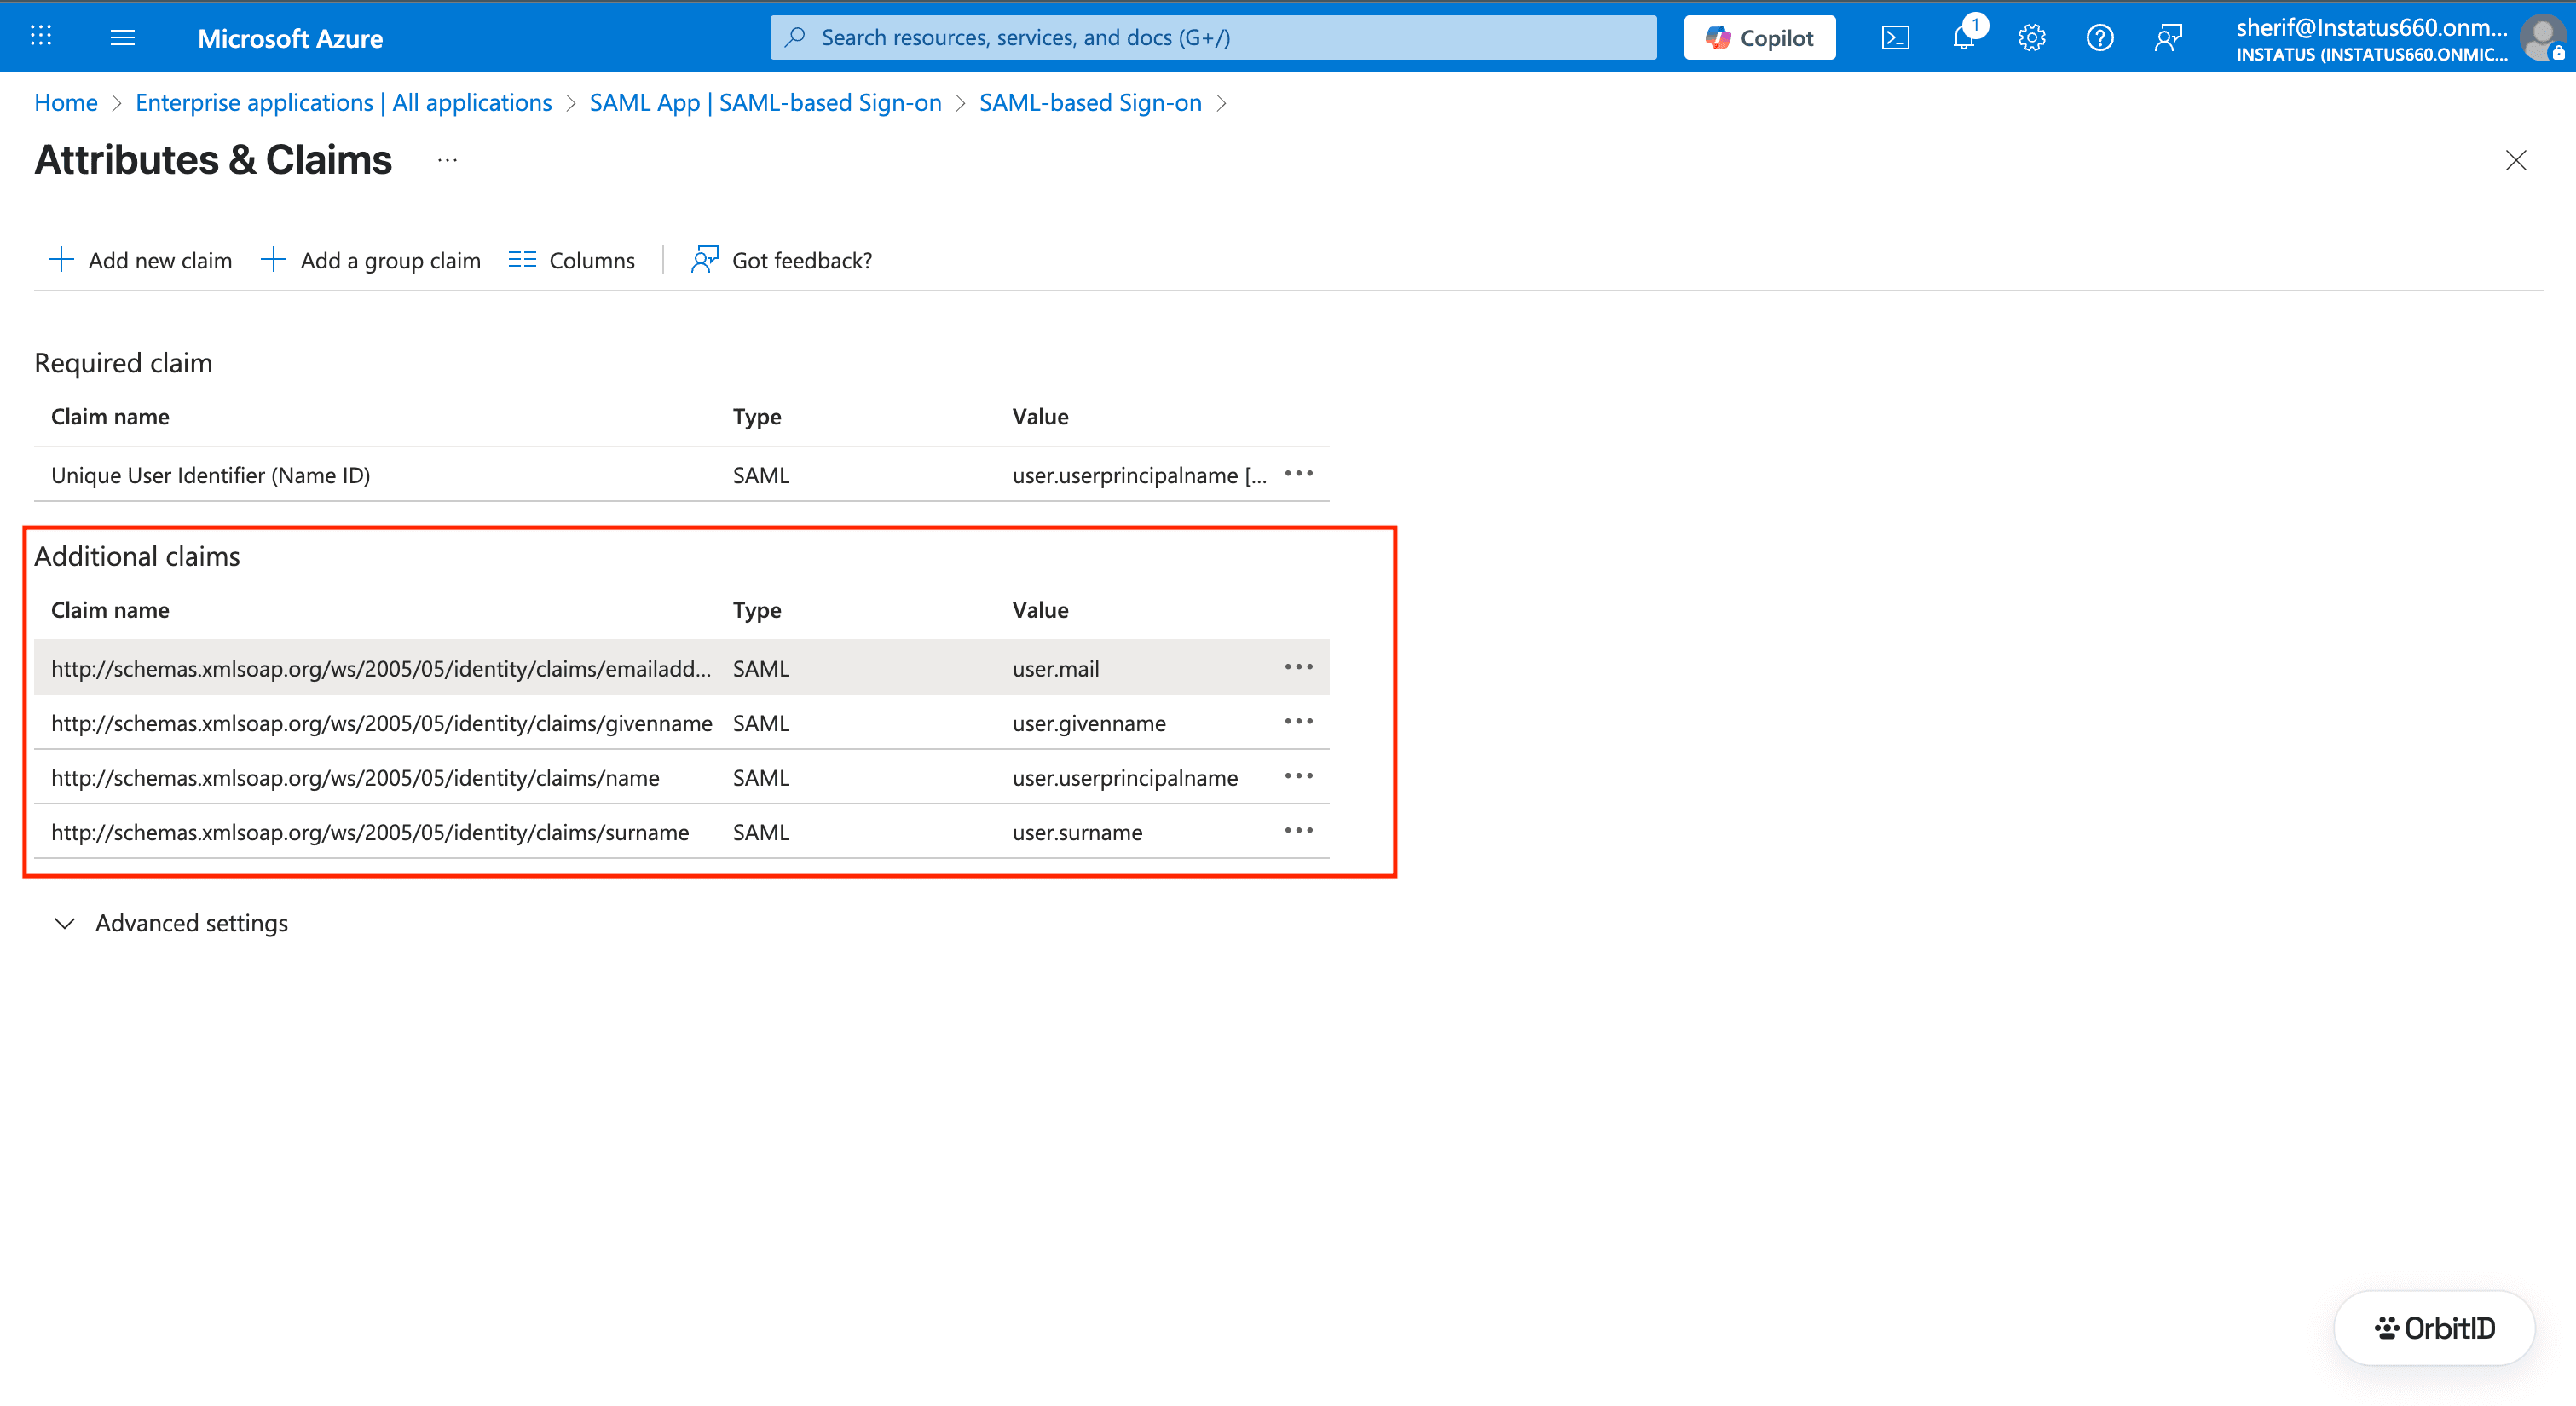
You have to configure the following attributes under the Attributes & Claims section:
| Name | Value |
|---|---|
http://schemas.xmlsoap.org/ws/2005/05/identity/claims/emailaddress | user.mail |
http://schemas.xmlsoap.org/ws/2005/05/identity/claims/givenname | user.givenname |
http://schemas.xmlsoap.org/ws/2005/05/identity/claims/name | user.userprincipalname |
http://schemas.xmlsoap.org/ws/2005/05/identity/claims/surname | user.surname |
Step 4: Download the IdP metadata
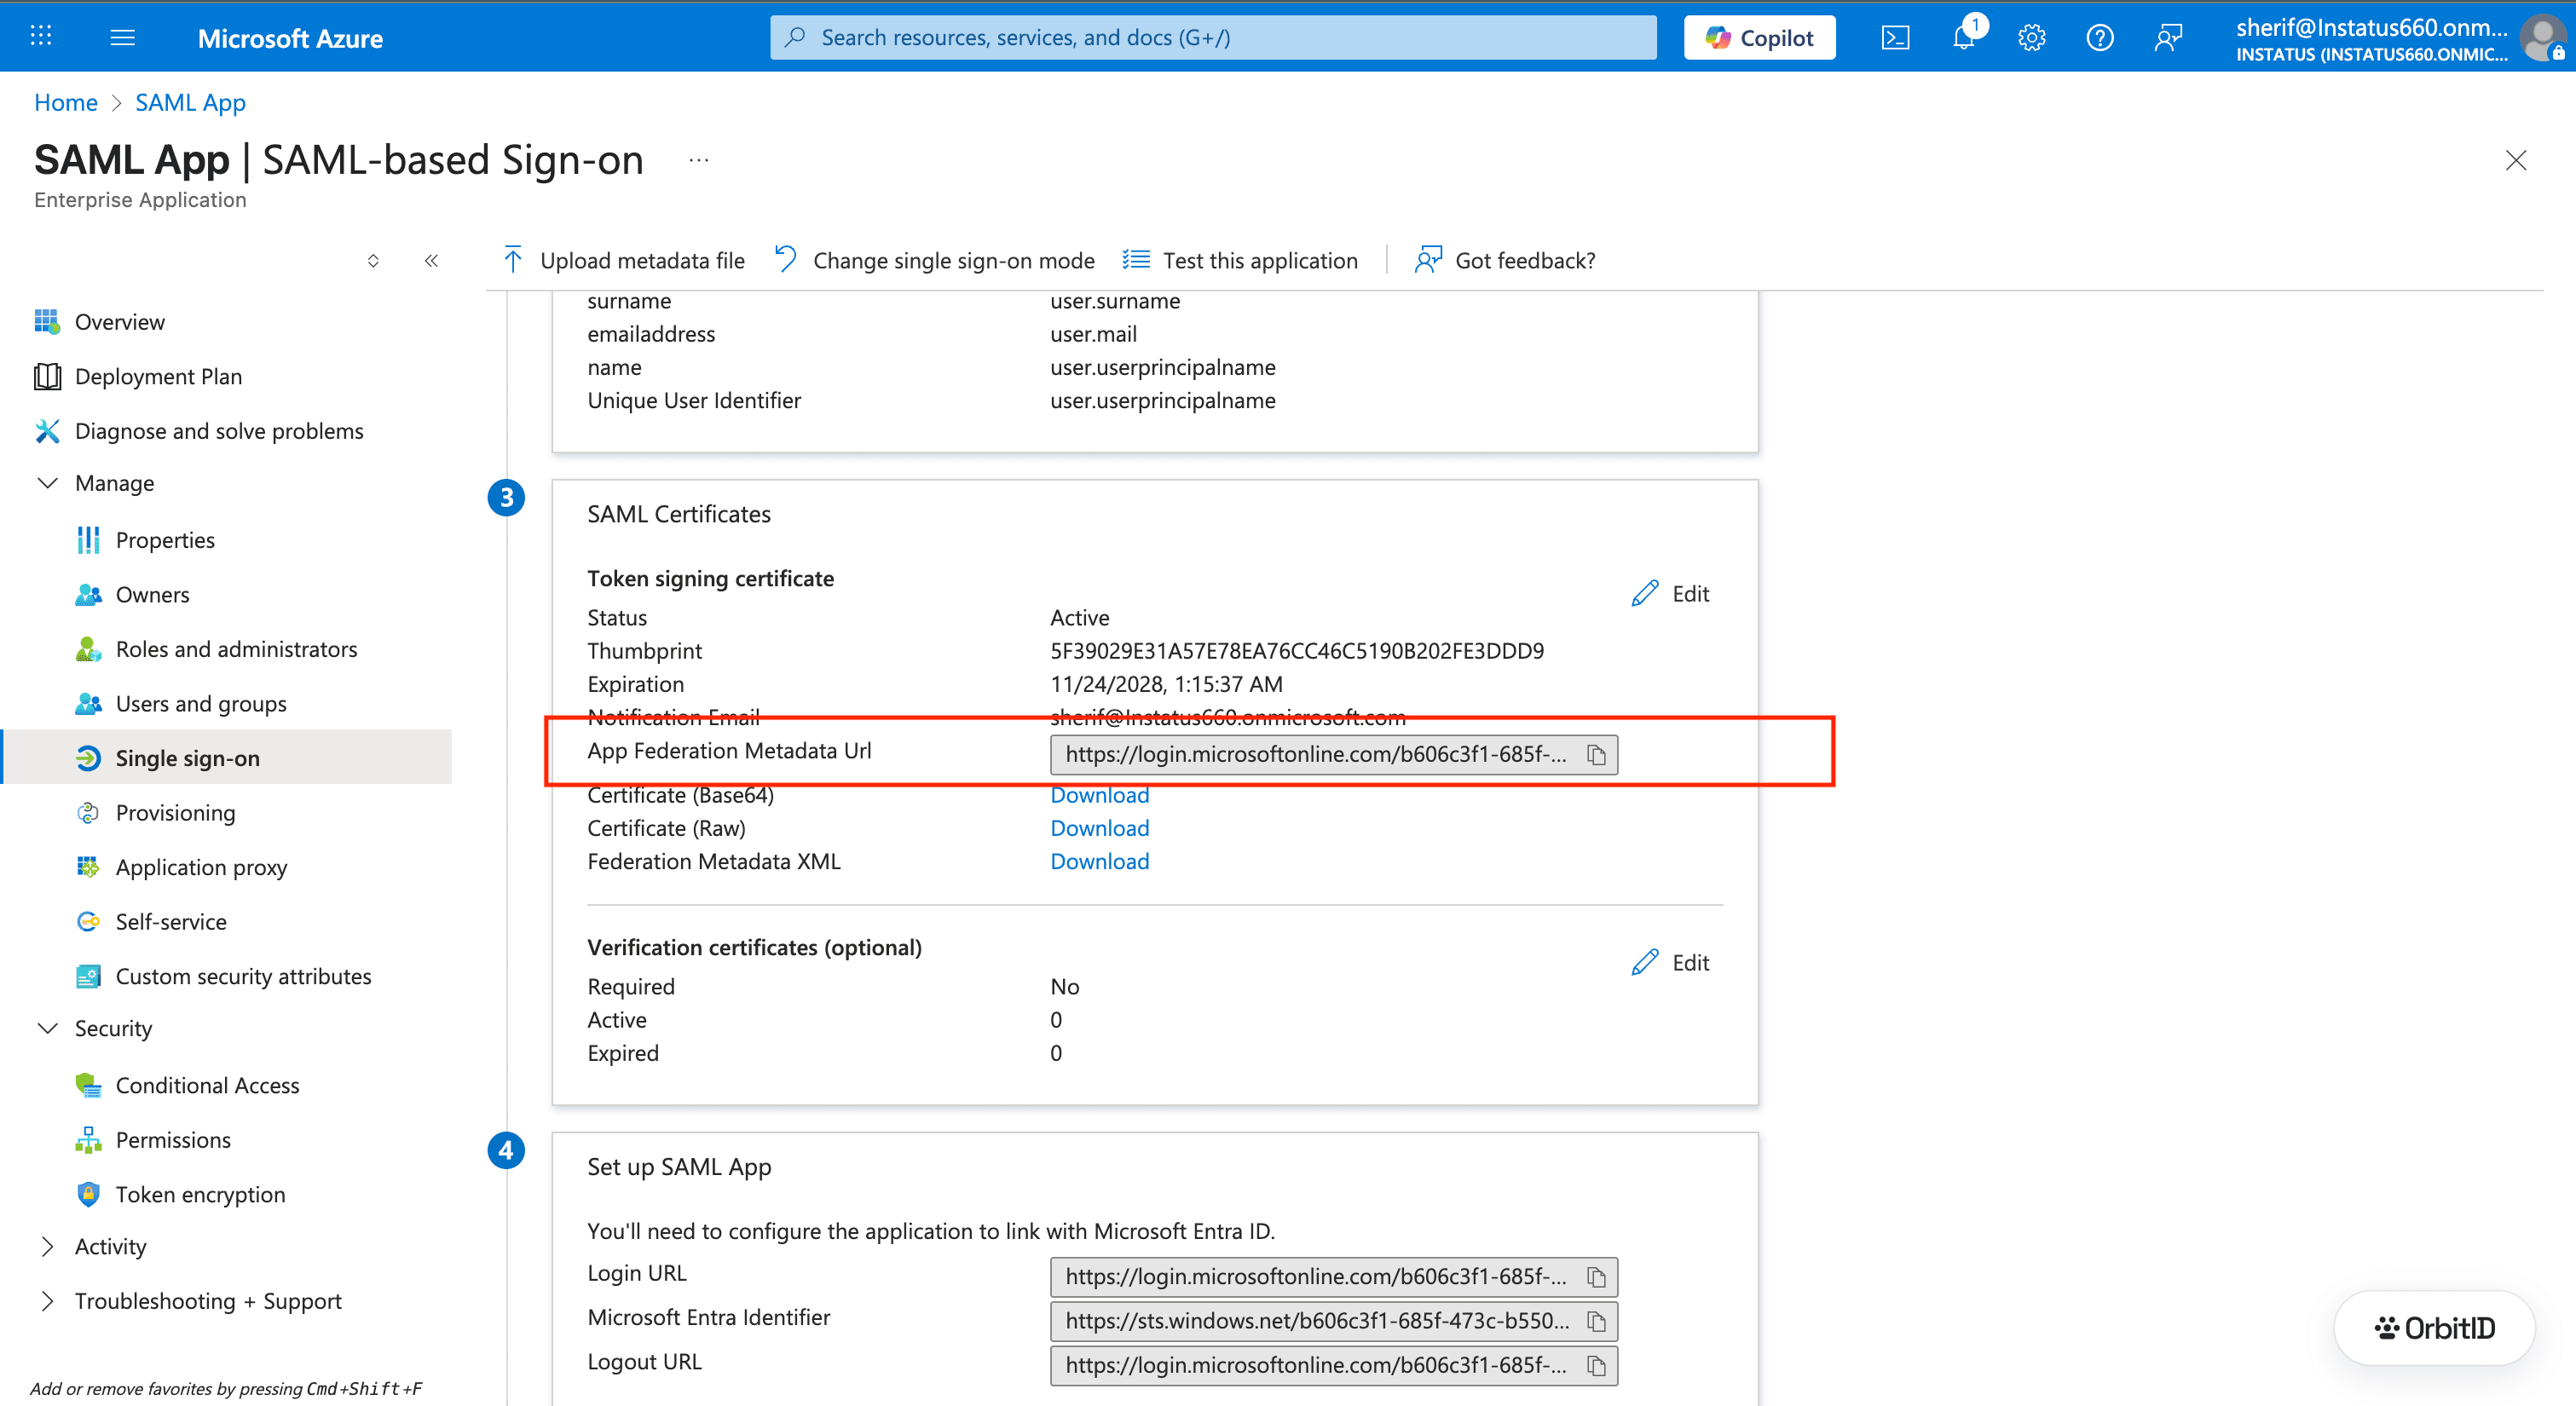
Go to the SAML Signing Certificate section and download the Federation Metadata XML, or copy the App Federation Metadata Url.
Finish in OrbitID
Finish in OrbitID: paste the IdP metadata URL or XML into the connection form (or the Admin Portal link). In the dashboard, open the environment, go to Connections, click New connection, choose SAML and paste the metadata URL or the XML you downloaded. If your customer's admin is following an Admin Portal link, they paste it into the final step of the portal instead.
You can also create the connection with the API: POST /api/v1/sso as described in the quickstart.